

Incident Response Plan: Complete Cybersecurity Guide
 Zahra_AlialialiOctober 19, 20266 Mins read23
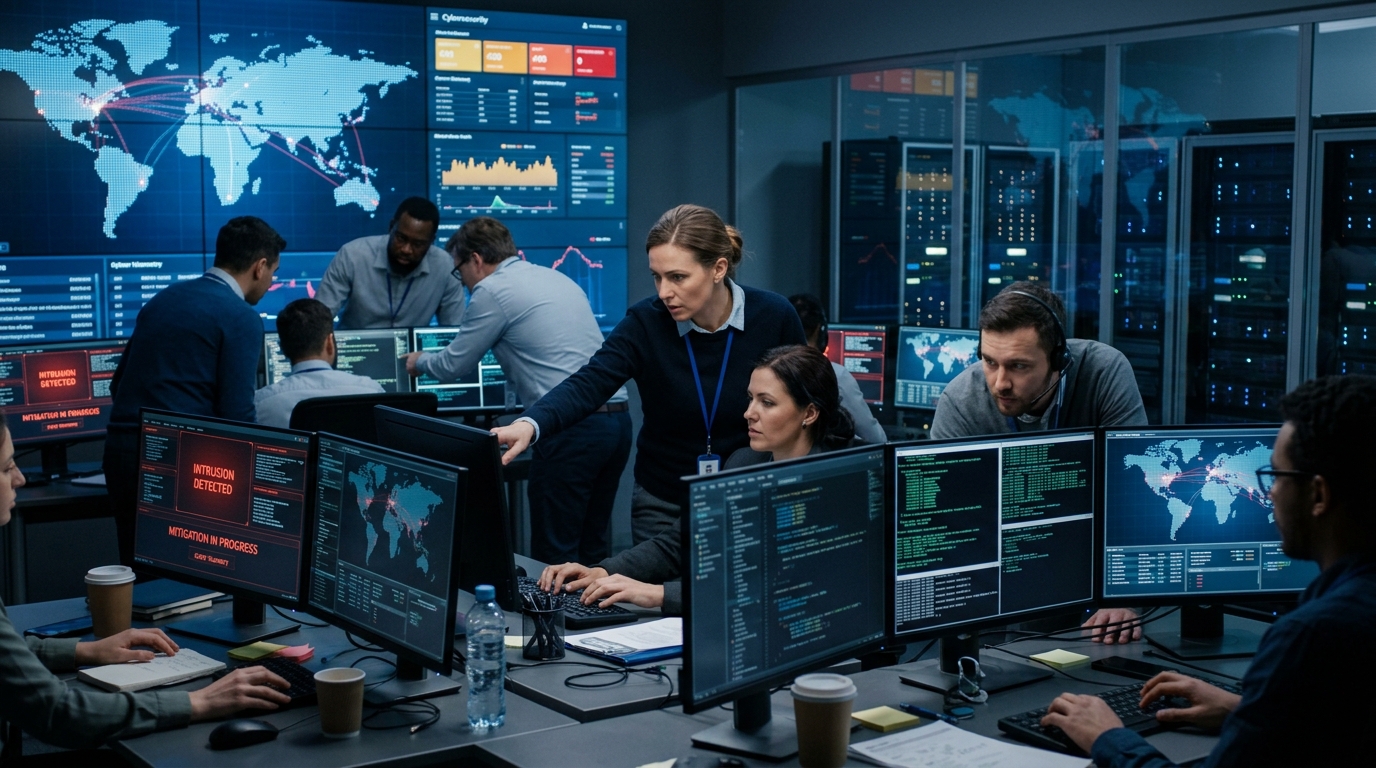
A cyberattack can happen even when an organization has strong security controls. A phishing email, compromised account, malware infection, or data breach can quickly become a serious business problem.
Without a clear plan, teams may waste valuable time deciding what to do next.
An incident response plan gives security teams a structured process for handling cybersecurity incidents. It defines responsibilities, communication procedures, investigation steps, containment actions, and recovery activities.
Organizations can use an incident response plan alongside cloud incident response procedures when incidents affect cloud-based systems.
This guide explains what an incident response plan is, what it should contain, how to create one, and how organizations can improve their incident response readiness.
What Is an Incident Response Plan?
An incident response plan is a documented set of procedures for detecting, investigating, containing, and recovering from cybersecurity incidents.
The plan helps security teams answer important questions:
- What happened?
- Who is responsible for responding?
- Which systems are affected?
- Who needs to be notified?
- How should the threat be contained?
- How can systems be safely restored?
A good plan reduces confusion during an incident and helps teams respond consistently.
Why Is an Incident Response Plan Important?
Cybersecurity incidents can develop quickly. Delays can increase the potential damage.
A documented plan can help organizations:
- Respond faster
- Reduce confusion
- Limit damage
- Protect critical systems
- Coordinate teams
- Improve communication
- Preserve evidence
- Recover more efficiently
It also gives employees clear instructions instead of requiring them to create a response process during an emergency.
What Should an Incident Response Plan Include?
A useful plan should cover the entire incident lifecycle.
Incident Response Team
Identify the people responsible for handling incidents.
Depending on the organization, this may include:
- Security analysts
- IT administrators
- Incident responders
- Management
- Legal professionals
- Communications staff
- Human resources
Each person should understand their responsibilities before an incident occurs.
Contact Information
Maintain current contact details for important team members and external providers.
Include:
- Primary contacts
- Backup contacts
- Security vendors
- Cloud providers
- Legal contacts
- Management
Contact information should be accessible even if normal corporate systems become unavailable.
Incident Classification
Not every security event requires the same response.
Organizations can classify incidents based on factors such as:
- Severity
- Number of affected systems
- Data involved
- Business impact
- Potential legal consequences
A critical breach should receive a different response from a low-risk security alert.
Incident Response Plan Steps
A practical plan commonly follows six stages.
1. Preparation
Preparation happens before an incident.
Organizations should:
- Define response roles.
- Document procedures.
- Protect important accounts.
- Enable appropriate logging.
- Maintain asset inventories.
- Prepare communication channels.
- Create response playbooks.
- Conduct training.
Preparation makes the later stages much easier.
2. Detection and Analysis
Security teams identify and investigate suspicious activity.
Possible sources include:
- SIEM alerts
- EDR alerts
- Firewall logs
- Cloud logs
- User reports
- Threat intelligence
Analysts should determine whether the event is a genuine incident and assess its scope.
Organizations can use security orchestration, automation and response to automate selected investigation tasks.
3. Containment
The goal is to stop the incident from spreading.
Depending on the situation, teams may:
- Isolate affected devices
- Disable compromised accounts
- Revoke credentials
- Block malicious connections
- Restrict network access
Containment should be carefully planned because aggressive actions can sometimes interrupt legitimate business operations.
4. Eradication
After containment, the organization removes the underlying threat.
This may include:
- Removing malware
- Deleting unauthorized accounts
- Patching vulnerabilities
- Rotating credentials
- Removing malicious files
- Correcting security weaknesses
Teams should confirm that the attacker no longer has access before moving forward.
5. Recovery
Recovery involves returning systems to normal operation.
Organizations may:
- Restore clean backups
- Rebuild compromised systems
- Validate security controls
- Monitor affected systems
- Gradually restore services
Recovery should include additional monitoring to detect signs of recurring compromise.
6. Lessons Learned
The final stage focuses on improving future security.
Teams should review:
- What caused the incident?
- How was it detected?
- How long did the attack continue?
- Which controls failed?
- What data was affected?
- What should change?
The findings should be added to future security improvements.
Incident Response Plan Template
Organizations can use this simple structure when creating a plan.
1. Purpose:
Explain the purpose and scope of the plan.
2. Incident Response Team:
List team members and responsibilities.
3. Incident Classification:
Define severity levels and escalation requirements.
4. Detection:
Document how incidents are identified.
5. Investigation:
Define evidence collection and analysis procedures.
6. Containment:
Document short-term and long-term containment actions.
7. Eradication:
Explain how threats and vulnerabilities will be removed.
8. Recovery:
Define system restoration and validation procedures.
9. Communication:
Specify internal and external notification requirements.
10. Documentation:
Record actions, findings, decisions, and timelines.
11. Lessons Learned:
Document improvements after the incident.
Communication During a Cybersecurity Incident
Communication is an important part of incident response.
Teams should know:
- Who communicates with management
- Who contacts affected employees
- Who handles customers
- Who communicates with legal teams
- Who manages public statements
Only authorized personnel should provide external statements.
Poor communication can create additional business and reputational risks during an incident.
Evidence Preservation
Some incidents require detailed investigation.
Teams should preserve relevant evidence before making changes that could destroy useful information.
Potential evidence includes:
- System logs
- Network records
- Emails
- Files
- Memory captures
- Authentication records
- Cloud activity
Organizations should document evidence handling and follow applicable legal and organizational requirements.
Incident Response Plan Best Practices
A strong plan should be practical rather than overly complicated.
Organizations should:
- Keep procedures clear.
- Assign specific responsibilities.
- Maintain current contact information.
- Define incident severity levels.
- Protect critical logs.
- Prepare communication procedures.
- Create playbooks for common incidents.
- Test the plan regularly.
- Update the plan after major incidents.
- Train relevant employees.
Regular testing is especially important. A plan that exists only as a document may not work effectively during a real attack.
Common Incident Response Mistakes
No Clear Ownership
If nobody knows who leads the response, valuable time can be lost.
Outdated Contact Information
An emergency contact list is useless if the listed people or numbers are no longer correct.
Ignoring Evidence
Making changes before preserving important evidence can complicate investigations.
No Communication Plan
Teams may provide inconsistent information without predefined communication procedures.
Never Testing the Plan
Organizations may discover serious gaps only after a real incident occurs.
Treating Every Incident the Same
Severity-based procedures help organizations prioritize resources.
Incident Response Plan Checklist
Use this checklist to review your plan:
- Are response roles clearly assigned?
- Are emergency contacts current?
- Are incidents classified by severity?
- Are detection procedures documented?
- Are investigation steps defined?
- Are containment actions documented?
- Are evidence-preservation procedures included?
- Is there a communication process?
- Are recovery procedures documented?
- Is the plan tested regularly?
- Are lessons from previous incidents incorporated?
How Often Should an Incident Response Plan Be Updated?
Organizations should review their plan regularly and whenever significant changes occur.
Updates may be necessary after:
- Major security incidents
- New cloud deployments
- Changes to security tools
- Organizational changes
- New regulatory requirements
- Changes to critical applications
Testing can also reveal areas that need improvement.
Conclusion
An incident response plan gives organizations a structured approach for handling cybersecurity incidents. It defines responsibilities and provides clear procedures for preparation, detection, analysis, containment, eradication, recovery, and lessons learned.
A useful plan should be simple enough to follow during a stressful incident while covering the systems, people, and processes that matter most.
Organizations should also connect their response procedures with data loss prevention and other security controls to reduce the impact of incidents involving sensitive information.
Finally, combining an incident response plan with continuous threat exposure management can help organizations identify weaknesses before attackers exploit them.
The most important step is not simply creating the document. Test it, update it, and make sure the people responsible for responding actually know how to use it.
FAQs
What is an incident response plan?
An incident response plan is a documented process that explains how an organization detects, investigates, contains, eliminates, and recovers from cybersecurity incidents.
Why does an organization need an incident response plan?
It provides clear responsibilities and procedures, helping teams respond faster and reduce confusion and potential damage during a security incident.
What are the main steps of incident response?
The main stages are preparation, detection and analysis, containment, eradication, recovery, and lessons learned.
Who should be part of an incident response team?
Depending on the organization, the team may include security professionals, IT staff, management, legal personnel, communications staff, and other relevant specialists.
What is an incident response plan template?
It is a structured framework organizations can use to document their incident response procedures, responsibilities, communication processes, and recovery steps.
How often should an incident response plan be tested?
Organizations should test their plans regularly and after major changes or incidents. Tabletop exercises can help identify weaknesses without disrupting production systems.
What should happen after a cybersecurity incident?
Teams should investigate the root cause, assess the impact, document findings, remediate weaknesses, and update security procedures based on lessons learned.
Is an incident response plan only for large companies?
No. Organizations of all sizes can benefit from an incident response plan. Smaller businesses can create a simpler plan based on their most important systems, data, and risks.

Security Operations Center Tools: Complete Guide
A Security Operations Center, or SOC, monitors an organization's systems for suspicious...
Zahra_Alialiali6 Mins read
Cloud Incident Response: Complete Guide
Cloud environments allow businesses to scale applications quickly, but they also create...
Zahra_Alialiali6 Mins read
Cloud Security Architecture: Complete Guide
Cloud environments give organizations flexibility, scalability, and access to powerful computing resources....
Zahra_Alialiali6 Mins read

Cloud Access Security Broker: Complete Guide
Cloud applications have become essential for modern businesses. Employees use SaaS platforms...
Zahra_Alialiali8 Mins read



Leave a comment