

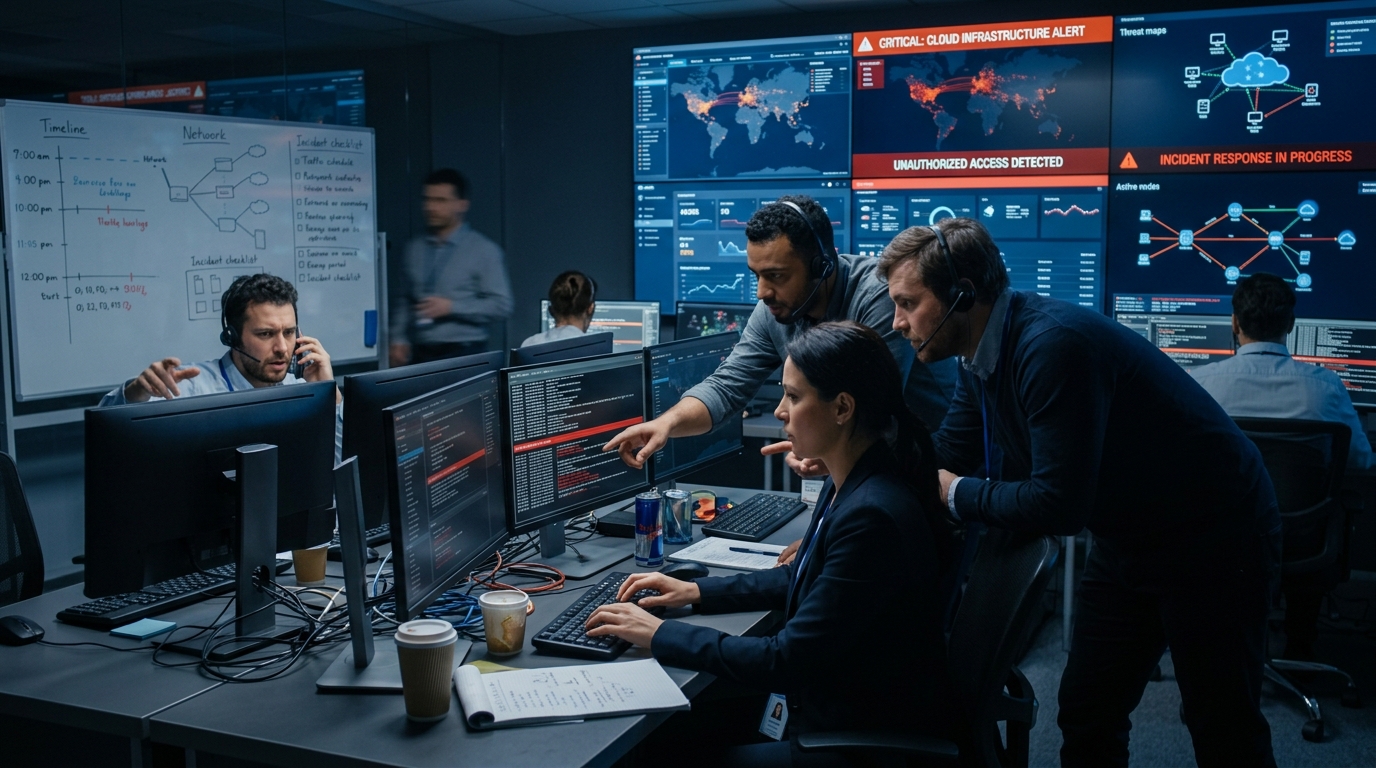
Cloud environments allow businesses to scale applications quickly, but they also create new security challenges. A compromised cloud account, exposed storage resource, malicious workload, or abused API can potentially give attackers access to sensitive systems and data.
When an incident occurs, security teams need a structured process for investigating what happened, limiting the damage, removing the threat, and restoring normal operations.
This process is known as cloud incident response.
Unlike traditional incident response, cloud investigations often involve temporary resources, distributed infrastructure, cloud APIs, identity systems, and large amounts of activity data. Security teams therefore need cloud-specific procedures and visibility.
A strong cloud security architecture provides an important foundation, but organizations also need an effective response plan for incidents that bypass preventive controls.
This guide explains cloud incident response, common cloud incidents, the response lifecycle, important tools, best practices, and how organizations can prepare for cloud-based attacks.
What Is Cloud Incident Response?
Cloud incident response is the process of preparing for, detecting, investigating, containing, and recovering from cybersecurity incidents affecting cloud environments.
A cloud incident could involve:
- A compromised user account
- Stolen credentials
- Exposed cloud storage
- Malware
- Data theft
- Unauthorized API activity
- Cryptomining
- Vulnerable workloads
- Misconfigured resources
The goal is to limit damage and restore secure operations as quickly as possible.
Cloud incident response also helps organizations learn from incidents so they can improve security controls and reduce the chance of similar attacks happening again.
Why Is Cloud Incident Response Important?
Cloud environments can change rapidly.
Resources may be:
- Created automatically
- Deleted quickly
- Moved between environments
- Scaled dynamically
- Managed through APIs
This can make investigations more difficult.
For example, an attacker may create a temporary cloud resource, use it for malicious activity, and delete it before a security analyst begins an investigation.
Effective response therefore requires:
- Centralized logging
- Identity visibility
- Asset inventories
- Monitoring
- Defined response procedures
- Regular testing
Common Cloud Security Incidents
Compromised Cloud Accounts
Attackers may obtain credentials through phishing, malware, credential theft, or other techniques.
Once inside an account, they may attempt to:
- Access sensitive resources
- Create new accounts
- Change permissions
- Steal data
- Disable security controls
Data Exposure
Cloud storage can accidentally become publicly accessible.
Sensitive information may include:
- Customer records
- Financial information
- Business documents
- Credentials
- Intellectual property
Security teams need to identify the exposed resource, determine what data was accessible, and contain the exposure.
Malicious Cloud Workloads
Attackers may compromise virtual machines or containers and use them for:
- Malware
- Cryptomining
- Credential theft
- Further attacks
Organizations can use a cloud workload protection platform to improve workload visibility and detection.
API Abuse
Cloud environments rely heavily on APIs.
Attackers may exploit weak authentication, stolen credentials, excessive permissions, or application vulnerabilities to abuse cloud APIs.
Cryptomining
Attackers sometimes compromise cloud accounts and deploy cryptocurrency-mining workloads.
Unexpected increases in cloud resource usage or billing can provide an early warning.
Cloud Incident Response Lifecycle
A structured response process helps teams manage incidents consistently.
Preparation
Preparation happens before an incident occurs.
Organizations should:
- Create an incident response plan.
- Identify critical cloud resources.
- Enable appropriate logging.
- Establish communication procedures.
- Define response responsibilities.
- Maintain current asset inventories.
- Test response procedures.
Teams should also identify which actions require approval before an emergency occurs.
Detection and Analysis
Security teams investigate alerts and determine whether an incident is occurring.
Useful information may include:
- Authentication events
- API activity
- Network connections
- Resource changes
- User behavior
- Workload activity
Analysts should establish:
- What happened?
- When did it happen?
- Which accounts were involved?
- Which resources were affected?
- What data may be at risk?
Containment
The objective is to stop the incident from spreading or causing additional damage.
Depending on the situation, containment may involve:
- Disabling compromised credentials
- Revoking sessions
- Restricting permissions
- Isolating workloads
- Blocking malicious connections
- Restricting network access
Teams should carefully document containment actions because aggressive changes can sometimes disrupt legitimate operations.
Eradication
After containment, teams remove the attacker’s access and underlying cause.
This may involve:
- Removing malicious resources
- Deleting unauthorized accounts
- Rotating credentials
- Patching vulnerabilities
- Removing malware
- Correcting cloud configurations
Recovery
Recovery returns affected systems to secure operation.
Teams may:
- Restore services
- Rebuild compromised workloads
- Validate security controls
- Monitor affected systems
- Confirm that unauthorized access has ended
Recovery should not simply restore the previous state if that state contained the original vulnerability.
Post-Incident Analysis
After the incident, security teams should determine:
- What caused the incident?
- Which controls failed?
- How was the attacker detected?
- How long did the attack last?
- What data or resources were affected?
- What should change?
The findings can improve future prevention and response.
Cloud Logs and Monitoring
Logs are essential for cloud investigations.
Security teams may need visibility into:
- Login activity
- API calls
- Administrative changes
- Network activity
- Resource creation
- Permission changes
- Application activity
Logs should be protected against unauthorized modification and retained according to organizational requirements.
Centralizing important security data can make investigations faster and help analysts reconstruct attacker activity.
Identity and Access During Cloud Incidents
Identity is particularly important during cloud incidents.
If an attacker compromises a privileged account, they may be able to make significant changes quickly.
Response plans should therefore address:
- Credential revocation
- Session termination
- Permission changes
- Privileged account protection
- Authentication monitoring
Organizations should maintain emergency procedures for securing important accounts without unnecessarily disrupting legitimate operations.
Incident Response Automation
Cloud environments generate large numbers of security events.
Automation can help with repetitive response tasks.
For example, a security orchestration platform could:
- Receive a high-confidence alert.
- Gather account and resource information.
- Check threat intelligence.
- Create an incident ticket.
- Alert the security team.
- Request approval for containment.
- Record the response actions.
Automation can improve response speed, but high-impact actions should have appropriate safeguards.
Cloud Incident Response vs Traditional Incident Response
Traditional incident response often focuses on physical or on-premises infrastructure.
Cloud environments introduce additional considerations, including:
- Cloud APIs
- Temporary resources
- Shared responsibility models
- Cloud identities
- Provider-specific logs
- Multi-cloud environments
- Automated infrastructure
The fundamental incident response principles remain similar, but cloud investigations require additional knowledge of cloud architecture and provider services.
Cloud Incident Response Best Practices
Organizations can improve their response capabilities by:
- Maintaining an up-to-date incident response plan.
- Centralizing important cloud logs.
- Protecting privileged accounts.
- Using strong authentication.
- Maintaining cloud asset inventories.
- Defining emergency access procedures.
- Testing response playbooks.
- Establishing clear escalation paths.
- Monitoring unusual API activity.
- Regularly reviewing permissions.
- Documenting incidents thoroughly.
Organizations should also connect incident response with cloud detection and response capabilities to improve detection and investigation.
Common Cloud Incident Response Mistakes
Waiting Until an Incident Happens
Organizations should prepare response procedures before an attack occurs.
Insufficient Logging
Without useful logs, determining what happened can become extremely difficult.
Ignoring Identity
Cloud attacks frequently involve compromised credentials and excessive permissions.
Over-Automating Response
Automatically taking disruptive actions without sufficient confidence can create additional problems.
Failing to Test the Plan
An incident response plan that has never been tested may not work as expected during a real emergency.
Not Learning From Incidents
Organizations should use post-incident findings to improve their security architecture and processes.
Cloud Incident Response Checklist
Use this checklist to assess your readiness:
- Is there a documented cloud incident response plan?
- Are critical cloud resources identified?
- Are important logs enabled?
- Are privileged accounts protected?
- Can compromised credentials be revoked quickly?
- Are cloud assets continuously monitored?
- Are response responsibilities clearly assigned?
- Are containment procedures documented?
- Are incident response playbooks tested?
- Is post-incident analysis performed?
Future of Cloud Incident Response
Cloud environments are becoming increasingly automated, while artificial intelligence is generating new security challenges and opportunities.
AI can help security teams:
- Analyze large volumes of security events
- Identify unusual behavior
- Prioritize alerts
- Summarize investigations
- Recommend response actions
Automation may also allow organizations to respond to high-confidence incidents faster.
However, organizations still need human oversight for complex incidents, especially when response actions could affect critical business systems.
Conclusion
Cloud incident response provides organizations with a structured way to handle cybersecurity incidents affecting cloud environments.
Preparation, detection, analysis, containment, eradication, recovery, and post-incident review all play important roles in reducing the impact of an attack.
Cloud-specific visibility is essential because attackers can abuse identities, APIs, workloads, and rapidly changing resources. Organizations should therefore combine strong preventive controls with continuous monitoring and well-tested response procedures.
Connecting incident response with continuous threat exposure management can also help organizations identify and prioritize weaknesses before they become incidents.
Ultimately, effective cloud incident response is about being prepared before an attack happens, responding quickly when something goes wrong, and using every incident as an opportunity to strengthen cloud security.
FAQs
What is cloud incident response?
Cloud incident response is the process of preparing for, detecting, investigating, containing, and recovering from cybersecurity incidents affecting cloud environments.
What are common cloud security incidents?
Common incidents include compromised accounts, data exposure, malicious workloads, API abuse, malware, unauthorized access, and cryptomining.
Why is cloud incident response different?
Cloud environments use dynamic resources, APIs, cloud identities, distributed infrastructure, and provider-specific logging, which can create additional investigation and response requirements.
What are the main stages of cloud incident response?
The main stages are preparation, detection and analysis, containment, eradication, recovery, and post-incident analysis.
Why are cloud logs important during an incident?
Logs help security teams reconstruct activity, identify affected resources, understand attacker behavior, and determine the scope of an incident.
Can cloud incident response be automated?
Yes. Organizations can automate repetitive investigation and response tasks, but high-impact actions should have appropriate safeguards and human oversight.
How can organizations prepare for cloud incidents?
They should create response plans, protect identities, enable appropriate logging, inventory cloud resources, define responsibilities, and regularly test response procedures.
What should organizations do after a cloud security incident?
Teams should determine the root cause, assess the impact, identify failed controls, remediate weaknesses, document findings, and update security procedures to reduce future risk.

Security Operations Center Tools: Complete Guide
A Security Operations Center, or SOC, monitors an organization's systems for suspicious...
 Zahra_Alialiali6 Mins read
Incident Response Plan: Complete Cybersecurity Guide
A cyberattack can happen even when an organization has strong security controls....
Zahra_Alialiali6 Mins read
Cloud Security Architecture: Complete Guide
Cloud environments give organizations flexibility, scalability, and access to powerful computing resources....
Zahra_Alialiali6 Mins read

Cloud Access Security Broker: Complete Guide
Cloud applications have become essential for modern businesses. Employees use SaaS platforms...
Zahra_Alialiali8 Mins read


Leave a comment