

LLM Security Risks: Complete Cybersecurity Guide
 Zahra_AlialialiNovember 2, 20266 Mins read10

Large language models (LLMs) can write text, analyze information, summarize documents, answer questions, and support business workflows. As organizations connect these models to sensitive data and external tools, however, new security concerns can appear.
Understanding LLM security risks is therefore essential for businesses that use generative AI.
Some risks affect the model itself. Others come from the application surrounding it, including data sources, APIs, plugins, user permissions, and connected tools.
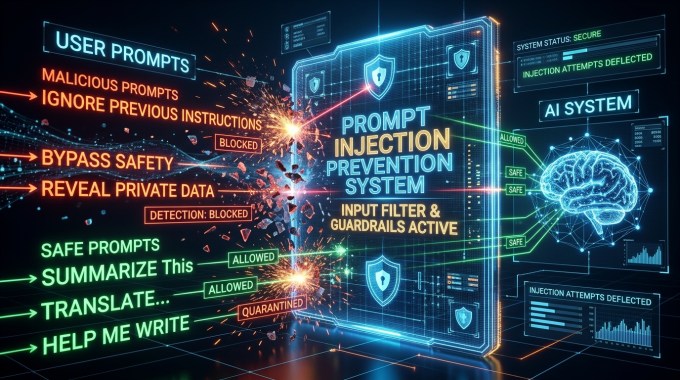
For example, prompt injection prevention can reduce the risk of malicious instructions manipulating an AI application.
This guide explains the major LLM security risks and practical ways organizations can reduce them.
What Are LLM Security Risks?
LLM security risks are threats that can affect large language models, the applications built around them, or the data and systems they interact with.
These risks can involve:
- Sensitive data
- User prompts
- Training data
- Model outputs
- External tools
- APIs
- Plugins
- Cloud services
- AI agents
The potential impact depends on how an organization deploys the LLM.
A simple chatbot may have limited access to sensitive systems. An AI agent connected to databases and business applications can create much greater exposure.
Why Do LLM Security Risks Matter?
LLMs introduce a different type of security challenge because they process natural language.
Traditional software usually follows clearly defined commands. An LLM, by contrast, interprets text and generates responses based on context.
That flexibility creates useful capabilities, but it also creates opportunities for manipulation.
Security teams should consider what happens if an attacker:
- Provides malicious instructions
- Uploads harmful content
- Extracts sensitive information
- Manipulates an AI agent
- Abuses connected tools
- Exploits a vulnerable AI application
A strong security strategy should address these risks before deployment.
Prompt Injection
Prompt injection is one of the most widely discussed LLM security risks.
An attacker can introduce instructions designed to influence an AI system’s behavior. Those instructions may appear directly in a user prompt or inside external content.
For example, a malicious webpage could contain instructions that attempt to manipulate an AI assistant while it processes the page.
The consequences depend on the application’s permissions and security controls.
Organizations should therefore combine input handling with access controls, tool validation, and monitoring.
For a deeper explanation, see our guide to prompt injection attack.
Sensitive Information Disclosure
LLM applications may process confidential information.
That information could include:
- Customer records
- Financial information
- Business documents
- Passwords
- Internal communications
- Personal information
Poor access controls or unsafe application design can expose sensitive data through prompts or generated responses.
Organizations should limit the information available to an LLM and apply appropriate authorization controls.
Data should only reach the model when it is necessary for the task.
Insecure LLM Outputs
An LLM can generate incorrect, unsafe, or manipulated content.
The risk increases when another application automatically trusts the output.
For example, an application might pass AI-generated instructions directly to a database, command system, or business workflow without checking them.
Output validation can reduce this risk.
Sensitive actions should also require appropriate authorization before execution.
Training Data Poisoning
Training data can influence how an LLM behaves.
If attackers introduce malicious or misleading information into training or fine-tuning data, they may influence the resulting model.
This type of manipulation can affect:
- Model behavior
- Accuracy
- Responses
- Security decisions
Organizations should therefore evaluate the sources used for training and fine-tuning.
Data provenance and quality controls are important parts of AI security.
Model Manipulation
Attackers may attempt to influence model behavior through carefully designed inputs or other techniques.
The goal could involve:
- Bypassing restrictions
- Producing unwanted content
- Changing responses
- Extracting information
- Influencing downstream decisions
Security testing can help identify weaknesses before deployment.
However, testing should consider the entire application rather than only the model.
Excessive Agency
An LLM becomes more powerful when it can perform actions through connected tools.
An AI agent might be able to:
- Search the internet
- Read files
- Access databases
- Send emails
- Call APIs
- Modify records
Excessive permissions can increase the impact of an attack.
The principle of least privilege is therefore important. Agents should only receive the permissions they genuinely need.
High-risk actions may also require human approval.
Insecure Plugins and Tools
LLM applications often connect to third-party tools and services.
These integrations can introduce additional attack surfaces.
Security teams should evaluate:
- API permissions
- Authentication
- Data access
- Tool inputs
- Tool outputs
- Third-party security
A compromised or poorly secured integration could create risks beyond the LLM itself.
LLM Supply Chain Risks
Organizations may rely on external models, datasets, libraries, APIs, and AI services.
Each dependency can introduce security concerns.
Supply chain risks may involve:
- Malicious components
- Vulnerable libraries
- Compromised models
- Untrusted datasets
- Insecure third-party services
Organizations should understand where their AI components come from and monitor important dependencies.
Model Theft and Extraction
LLMs can require significant resources to develop and train.
Attackers may attempt to extract information about a model or reproduce its behavior through repeated queries.
Model theft can create intellectual property concerns and increase the risk of unauthorized use.
Organizations should monitor unusual usage patterns and apply suitable access controls.
RAG Security Risks
Retrieval-Augmented Generation (RAG) allows an LLM to retrieve information from external sources.
This can improve responses, but it also introduces additional security concerns.
Retrieved information may contain:
- Incorrect data
- Sensitive information
- Malicious instructions
- Outdated content
Applications should treat retrieved content carefully and enforce access controls before providing information to the model.
LLM Risks in AI Agents
AI agents can perform tasks instead of simply generating text.
That capability creates additional risks because an agent may have access to external systems.
A malicious instruction could potentially influence an agent’s actions if the application lacks appropriate controls.
Developers should limit permissions, validate tool calls, monitor actions, and require approval for high-impact operations.
Shadow AI
Employees may use public AI tools without organizational approval.
This practice is often called Shadow AI.
Employees might accidentally submit:
- Customer information
- Internal documents
- Source code
- Financial information
- Confidential business data
Organizations can reduce this risk through clear AI policies, employee training, approved tools, and data protection controls.
How to Reduce LLM Security Risks
A layered security strategy provides stronger protection.
Limit Data Access
Give the model only the information needed for its task.
Apply Least Privilege
Restrict what AI agents, tools, and integrations can access.
Validate Inputs and Outputs
Check important data before the model processes it and before another system acts on its output.
Secure APIs and Tools
Use authentication, authorization, rate limits, and monitoring for connected services.
Monitor AI Activity
Track important prompts, tool calls, data access, and unusual behavior.
Test AI Applications
Conduct security testing before deployment and after major changes.
Protect Sensitive Data
Use appropriate access controls, encryption, and data protection measures.
These controls align with a secure by design cybersecurity approach.
LLM Security Best Practices
Organizations can strengthen AI security by:
- Identify sensitive AI use cases.
- Classify data before connecting it to an LLM.
- Limit model and agent permissions.
- Treat external content as untrusted.
- Validate important outputs.
- Secure third-party integrations.
- Monitor AI activity.
- Test for prompt injection.
- Review AI dependencies.
- Train employees on safe AI usage.
- Update security controls as AI capabilities change.
Security teams should also include AI systems in their broader risk management processes.
LLM Security Checklist
Before deploying an LLM application, ask:
- What data can the model access?
- Is sensitive information protected?
- Can users manipulate the model?
- Is external content treated as untrusted?
- What tools can the AI access?
- Are tool calls validated?
- Are outputs checked?
- Are high-risk actions reviewed?
- Is AI activity logged?
- Are third-party dependencies secure?
- Has the application undergone security testing?
The Future of LLM Security
LLM security will become increasingly important as AI systems move deeper into business operations.
Future applications will likely combine models with agents, databases, APIs, cloud services, and automated workflows.
As these connections grow, security teams will need to protect not only the model but the entire AI ecosystem.
AI security testing, identity controls, data protection, monitoring, and application security will all play important roles.
Organizations should also review their controls whenever they introduce new models, tools, data sources, or agent capabilities.
Conclusion
LLM security risks extend beyond the AI model itself. They can involve sensitive data, prompts, outputs, external content, tools, APIs, agents, and third-party dependencies.
Prompt injection, data disclosure, insecure outputs, training data poisoning, excessive agency, and supply chain weaknesses can all create security challenges.
The best defense is a layered approach. Organizations should limit data access, apply least privilege, validate important inputs and outputs, secure integrations, monitor AI activity, and regularly test their applications.
Data protection is equally important. Strong data loss prevention controls can help organizations reduce the risk of sensitive information reaching inappropriate AI systems or users.
Ultimately, secure LLM deployment requires organizations to treat AI as part of the wider cybersecurity environment rather than as a standalone technology.
FAQs
What are LLM security risks?
LLM security risks are threats that can affect large language models, AI applications, their data, connected tools, and surrounding infrastructure.
What is the biggest LLM security risk?
There is no single risk that applies to every application. Prompt injection, sensitive information disclosure, excessive agency, and insecure integrations can become serious risks depending on the system’s design.
Can LLMs leak sensitive information?
Yes. Poor access controls, unsafe application design, or inappropriate data handling can expose sensitive information through AI interactions.
What is prompt injection in LLMs?
Prompt injection involves introducing instructions designed to manipulate an LLM or the application around it.
How can organizations secure LLM applications?
Organizations can use least privilege, data access controls, input and output validation, secure APIs, monitoring, security testing, and human approval for high-risk actions.
Are AI agents more risky than basic chatbots?
AI agents can create greater security risks because they may have access to external tools, databases, APIs, and business systems.
What is LLM supply chain security?
LLM supply chain security involves protecting the models, datasets, libraries, APIs, and third-party services used to build and operate AI applications.
Should companies include LLMs in cybersecurity risk assessments?
Yes. Organizations should evaluate LLMs and AI applications as part of their broader cybersecurity risk management process, especially when these systems handle sensitive data or control business workflows.
How Kids Bypass Android Parental Controls in 2027
Parents use parental controls to manage their children's screen time, block harmful...
 Beatriz4 Mins read

Vibe Coding: What Is It and Why Do Developers Love It?
Imagine building a website by describing what you want instead of writing...
Beatriz4 Mins read
Prompt Injection Attack: Complete Security Guide
Artificial intelligence systems can process large amounts of information and perform tasks...
Zahra_Alialiali7 Mins read

Genie 4: Google’s AI Creates Realistic Interactive Worlds
Google DeepMind has introduced Genie 4, an artificial intelligence model that creates...
Beatriz4 Mins read



Leave a comment