

Security Operations Center Analyst: Complete Career Guide for 2026
 Zahra_AlialialiJuly 16, 20265 Mins read141

Cyber threats have become more frequent, sophisticated, and costly than ever before. Organizations face constant risks from ransomware, phishing campaigns, insider threats, data breaches, and advanced persistent threats (APTs). To defend against these attacks, many businesses operate a Security Operations Center (SOC), where security professionals continuously monitor and respond to potential cyber threats. At the heart of this team is the Security Operations Center Analyst.
A SOC Analyst is responsible for monitoring security events, investigating suspicious activity, identifying threats, and helping organizations respond quickly to security incidents. As businesses continue expanding their digital infrastructure in 2026, demand for SOC Analysts remains strong across industries.
Whether you’re starting a cybersecurity career or exploring different security roles, becoming a Security Operations Center Analyst is one of the best entry points into the field.
What Is a Security Operations Center Analyst?
A Security Operations Center Analyst is a cybersecurity professional who monitors an organization’s networks, systems, and security tools to identify, investigate, and respond to potential cyber threats.
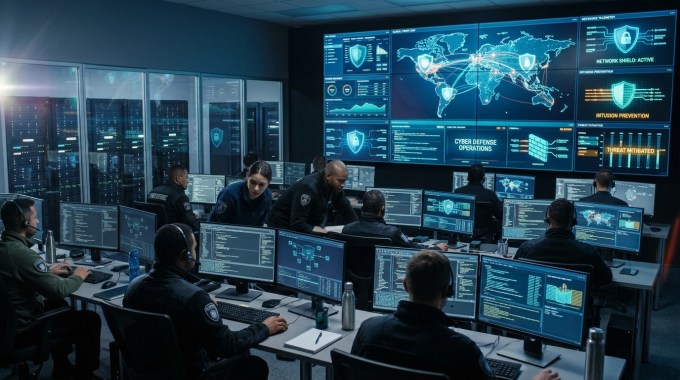
SOC Analysts work in dedicated Security Operations Centers where they monitor security alerts around the clock to help prevent attacks before they cause significant damage.
Their primary objective is to detect threats as early as possible and coordinate appropriate responses.
Why Security Operations Centers Are Important
Modern organizations generate millions of security events every day.
Without dedicated monitoring, businesses may struggle to detect:
- Malware infections
- Phishing attacks
- Unauthorized access
- Insider threats
- Data breaches
- Suspicious network activity
A Security Operations Center provides continuous visibility into an organization’s security environment.
Responsibilities of a Security Operations Center Analyst
Daily responsibilities vary depending on the organization and experience level.
Common duties include:
- Monitoring security alerts
- Investigating suspicious activity
- Reviewing system and network logs
- Escalating security incidents
- Supporting incident response
- Documenting investigations
- Identifying indicators of compromise (IOCs)
- Collaborating with security teams
Most entry-level analysts spend much of their time monitoring alerts generated by security tools.
Typical Daily Tasks
A Security Operations Center Analyst may begin the day by reviewing overnight security alerts.
Typical activities include:
- Reviewing SIEM dashboards
- Investigating login anomalies
- Examining suspicious network traffic
- Validating phishing reports
- Monitoring endpoint security alerts
- Updating incident documentation
Each investigation helps determine whether an alert represents a genuine security threat or a false positive.
Skills Required
Successful SOC Analysts combine technical knowledge with analytical thinking.
Technical Skills
Important technical skills include:
- Networking fundamentals
- Windows administration
- Linux basics
- TCP/IP
- DNS
- HTTP and HTTPS
- Firewall concepts
- Endpoint security
Understanding how computer systems communicate is essential.
Cybersecurity Skills
Employers commonly expect knowledge of:
- Threat detection
- Malware basics
- Phishing attacks
- Incident response
- Vulnerability management
- Identity and access management
These topics form the foundation of SOC work.
Soft Skills
SOC Analysts also need:
- Problem-solving
- Critical thinking
- Communication
- Attention to detail
- Teamwork
- Time management
Strong communication is particularly important during incident investigations.
Security Tools Used by SOC Analysts
A Security Operations Center Analyst works with a variety of security technologies.
Common tools include:
- SIEM platforms
- Endpoint Detection and Response (EDR)
- Firewalls
- Intrusion Detection Systems (IDS)
- Intrusion Prevention Systems (IPS)
- Threat intelligence platforms
- Email security solutions
Learning how these tools work improves investigation skills.
Common Security Threats Investigated
SOC Analysts frequently investigate:
- Phishing emails
- Malware infections
- Ransomware activity
- Credential theft
- Suspicious logins
- Unauthorized privilege changes
- Data exfiltration attempts
- Insider threats
Quick identification helps reduce organizational risk.
SOC Analyst Career Levels
Most Security Operations Centers use different analyst tiers.
Tier 1 SOC Analyst
Responsibilities include:
- Monitoring alerts
- Initial investigations
- Ticket creation
- Escalating serious incidents
- positions are excellent entry-level cybersecurity roles.
Tier 2 SOC Analyst
Analysts perform deeper investigations.
Responsibilities include:
- Threat analysis
- Incident investigation
- Malware analysis
- Threat hunting support
Tier 3 SOC Analyst
Senior analysts often handle:
- Advanced threat hunting
- Complex investigations
- Incident leadership
- Security improvements
- Threat intelligence
Career progression usually follows this structure.
Certifications That Help
Several certifications support a SOC career.
Popular beginner certifications include:
- CompTIA Security+
- ISC2 Certified in Cybersecurity (CC)
- Google Cybersecurity Certificate
- CompTIA Network+
- Microsoft SC-900
As experience grows, professionals often pursue advanced certifications.
How to Become a Security Operations Center Analyst
A common learning path includes:
Step 1: Learn Networking
Understand:
- TCP/IP
- DNS
- Routing
- Switching
- Network troubleshooting
Networking is the foundation of cybersecurity.
Step 2: Learn Operating Systems
Gain experience with:
- Windows
- Linux
- Active Directory
- Command-line tools
Operating system knowledge is essential for investigations.
Step 3: Study Cybersecurity Fundamentals
Focus on:
- Malware
- Phishing
- Access control
- Cryptography
- Risk management
Step 4: Practice Hands-On Skills
Build experience using:
- Home labs
- TryHackMe
- Hack The Box
- Blue Team Labs Online
- Security simulations
Practical experience greatly improves employability.
How AI Is Transforming Security Operations Centers
Artificial intelligence is changing cybersecurity in 2026.
SOC teams increasingly use AI-powered systems to:
- Detect anomalies
- Correlate security events
- Reduce false positives
- Prioritize alerts
- Support incident investigations
Although AI automates repetitive tasks, human analysts remain essential for decision-making and complex investigations.
Common Challenges
SOC Analysts often encounter:
- Alert fatigue
- False positives
- Large volumes of log data
- Evolving attack techniques
- Time-sensitive investigations
Developing analytical skills helps overcome these challenges.
Career Growth Opportunities
Starting as a Security Operations Center Analyst can lead to many advanced cybersecurity careers.
Popular career paths include:
- Senior SOC Analyst
- Incident Responder
- Threat Hunter
- Digital Forensics Analyst
- Malware Analyst
- Security Engineer
- Threat Intelligence Analyst
- Security Consultant
Many cybersecurity professionals begin their careers in a SOC.
Salary Expectations
Salary varies depending on:
- Country
- Experience
- Certifications
- Industry
- Employer
SOC Analysts generally receive competitive salaries, with significant earning potential as they progress into senior and specialized roles.
Future of Security Operations Centers
Security Operations Centers continue to evolve rapidly.
Major trends include:
- AI-assisted threat detection
- Extended Detection and Response (XDR)
- Cloud-native SOC platforms
- Zero Trust security
- Automated incident response
- Threat intelligence integration
These technologies help SOC teams respond to threats more efficiently.
Conclusion
A Security Operations Center Analyst plays a critical role in protecting organizations against cyber threats by monitoring security events, investigating suspicious activity, and supporting incident response efforts. As cyberattacks continue to increase in complexity, SOC Analysts remain among the most in-demand cybersecurity professionals.
In 2026, building strong networking knowledge, learning operating systems, gaining hands-on experience, and earning beginner certifications can help aspiring professionals start a successful career in a Security Operations Center. With continuous learning and practical experience, a SOC Analyst role can open the door to many advanced cybersecurity career opportunities.
FAQs
1. What does a Security Operations Center Analyst do?
A SOC Analyst monitors security alerts, investigates suspicious activity, responds to incidents, and helps protect an organization’s systems.
2. Is a SOC Analyst an entry-level cybersecurity job?
Yes. Many organizations consider Tier 1 SOC Analyst positions to be excellent entry-level cybersecurity roles.
3. What skills are needed to become a SOC Analyst?
Networking, Windows, Linux, security fundamentals, log analysis, communication, and problem-solving skills are important.
4. Which certifications help become a SOC Analyst?
CompTIA Security+, ISC2 Certified in Cybersecurity (CC), Google Cybersecurity Certificate, and CompTIA Network+ are popular beginner options.
5. What tools do SOC Analysts use?
Common tools include SIEM platforms, EDR solutions, IDS/IPS, firewalls, endpoint protection software, and threat intelligence platforms.
6. Is coding required for a SOC Analyst?
Basic scripting can be helpful, but strong networking and cybersecurity knowledge are generally more important for entry-level SOC roles.
7. Can AI replace SOC Analysts?
AI helps automate alert analysis and threat detection, but human analysts remain essential for investigations, decision-making, and incident response.
8. Is becoming a Security Operations Center Analyst a good career in 2026?
Yes. Demand for SOC Analysts continues to grow as organizations invest in stronger cybersecurity defenses and 24/7 security monitoring.



Computer Antivirus: How It Works and Do You Really Need It?
Your computer may store your photos, passwords, work files, and banking details....
 Beatriz3 Mins read
Workers Filming Their Jobs to Train AI: Will Robots Replace Them?
Workers in India are wearing cameras while doing everyday jobs. They film...
Beatriz5 Mins read

ConnectWise Cyber Breach: How Hackers Targeted 2,250 Companies
A major cyberattack on the IT company ConnectWise has exposed security risks...
Beatriz3 Mins read
PHP Security Flaws Force Websites Offline Worldwide
A critical security update for PHP has triggered emergency action across the...
Beatriz3 Mins read




Leave a comment