

Threat Hunting Techniques: Complete Guide
 Zahra_AlialialiOctober 22, 20266 Mins read65
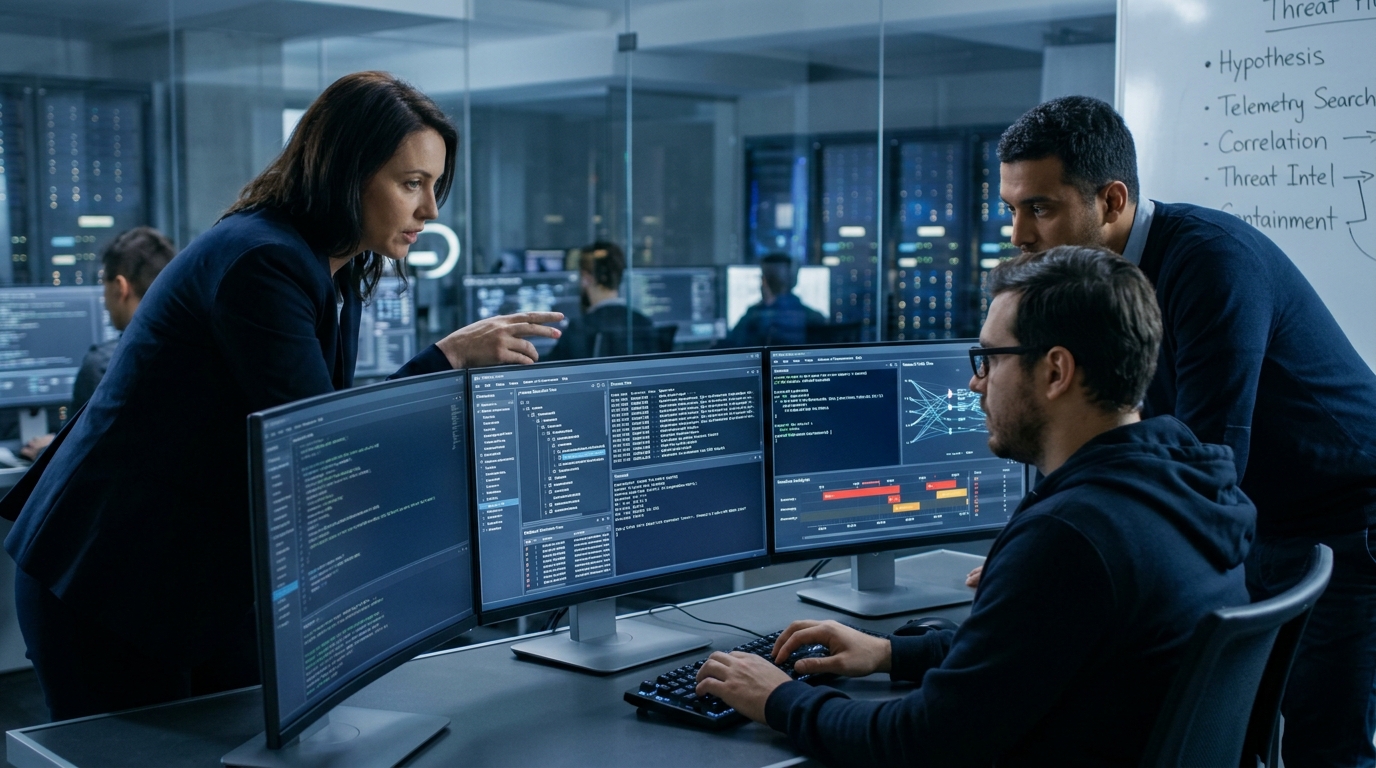
Cybersecurity tools can detect many threats automatically, but they cannot always identify every attack. Skilled security teams also search for suspicious activity that automated alerts may miss.
This proactive process is called threat hunting.
Threat hunting techniques help security professionals search for hidden attackers, unusual behavior, compromised accounts, and other signs of malicious activity. Instead of waiting for an alert, threat hunters actively look for evidence that something may be wrong.
Threat hunting works well alongside SOC analyst tools because analysts can use logs, endpoint data, network information, and other security telemetry during investigations.
This guide explains the main threat hunting techniques, how the process works, useful tools, practical examples, and best practices.
What Is Threat Hunting?
Threat hunting is a proactive cybersecurity activity that involves searching networks, endpoints, cloud environments, and other systems for threats that may have avoided existing security controls.
A threat hunter may investigate questions such as:
- Are attackers already inside the network?
- Are compromised accounts behaving unusually?
- Are systems communicating with suspicious destinations?
- Are unusual processes running?
- Has sensitive data been accessed unexpectedly?
Threat hunting does not replace automated detection. Instead, it adds a human-driven layer of investigation.
Why Are Threat Hunting Techniques Important?
Attackers can sometimes bypass security controls or remain undetected for extended periods.
Threat hunting helps organizations search for these hidden threats.
It can help security teams:
- Find previously unknown threats
- Detect compromised accounts
- Identify unusual behavior
- Discover security gaps
- Improve detection rules
- Investigate suspicious activity
- Reduce attacker dwell time
Hunting can also reveal weaknesses that should be addressed before they lead to a larger incident.
How Does Threat Hunting Work?
A typical hunt follows a structured process.
1. Create a Hypothesis
Hunters begin with a question or assumption that can be tested.
For example:
Could an attacker be using stolen credentials to access sensitive systems?
The team then identifies the data needed to investigate that possibility.
2. Collect Relevant Data
Hunters may examine:
- Endpoint telemetry
- Authentication logs
- DNS records
- Network traffic
- Cloud activity
- Application logs
- Threat intelligence
The quality of available data strongly affects the investigation.
3. Search for Evidence
Analysts query the available data for unusual patterns or indicators.
They may search for unexpected processes, authentication events, network connections, or file activity.
4. Investigate Findings
Potentially suspicious activity requires additional investigation.
Analysts compare the activity against normal behavior and other evidence.
5. Respond and Improve
If malicious activity is confirmed, the organization follows its incident response procedures.
Hunters should also use the findings to improve detection rules and security controls.
Common Threat Hunting Techniques
Hypothesis-Driven Hunting
This is one of the most common approaches.
The hunter starts with a specific security question and searches for evidence that supports or disproves it.
For example, a team may investigate whether attackers are abusing legitimate administrative tools.
This approach keeps investigations focused.
IOC-Based Hunting
Indicators of compromise, or IOCs, are clues associated with potentially malicious activity.
Examples include:
- IP addresses
- Domains
- URLs
- File hashes
- Email addresses
Hunters can search security data for known indicators.
IOC-based hunting can be useful, but indicators can change quickly. Threat hunters should therefore avoid relying only on known indicators.
TTP-Based Hunting
Tactics, techniques, and procedures (TTPs) describe how attackers operate.
Instead of searching for one specific malicious file or IP address, analysts look for behaviors associated with attack techniques.
For example, a hunter could investigate unusual credential access or suspicious administrative activity.
TTP-based hunting can remain useful even when attackers change their infrastructure.
Behavioral Hunting
Behavioral hunting focuses on unusual actions rather than specific indicators.
Examples include:
- An account accessing systems it rarely uses
- An unusual login time
- Unexpected administrative activity
- A workstation making unusual network connections
The goal is to identify activity that differs from expected behavior.
Anomaly-Based Hunting
Anomaly hunting searches for activity that falls outside a normal baseline.
For example, a device that normally communicates with a small group of internal systems might suddenly begin connecting to unfamiliar external destinations.
An anomaly does not automatically mean an attack. Analysts need additional evidence before reaching a conclusion.
Threat Intelligence-Driven Hunting
Threat intelligence can provide information about current attacker techniques, infrastructure, and campaigns.
Hunters can use this information to develop new hypotheses and search their environments for related activity.
A cyber threat intelligence program can therefore strengthen proactive hunting.
Network Threat Hunting
Network data can reveal suspicious communications that endpoint tools may not fully explain.
Hunters may investigate:
- DNS requests
- Unusual outbound connections
- Suspicious protocols
- Large data transfers
- Communication with known malicious infrastructure
Network hunting is especially useful when investigating command-and-control activity.
Endpoint Threat Hunting
Endpoint hunting focuses on computers, servers, and other devices.
Analysts may search for:
- Unusual processes
- Suspicious parent-child relationships
- Unexpected scripts
- Persistence mechanisms
- Abnormal file activity
EDR platforms can provide valuable endpoint telemetry for this type of investigation.
Identity Threat Hunting
Attackers often use stolen credentials to avoid traditional malware detection.
Identity hunting focuses on authentication and account activity.
Analysts can investigate:
- Impossible travel
- Unusual login locations
- Multiple failed logins
- Privilege changes
- Unusual access patterns
- Suspicious service accounts
This approach is increasingly important in cloud and remote-work environments.
Cloud Threat Hunting
Cloud environments create additional hunting opportunities.
Security teams can investigate:
- Unusual API calls
- New access keys
- Unexpected permission changes
- Suspicious cloud logins
- Unusual resource creation
- Abnormal data access
Cloud hunting requires visibility into cloud audit logs and identity activity.
Threat Hunting Tools
Threat hunters may use several types of security technology.
Common categories include:
- SIEM platforms
- EDR and XDR
- Network monitoring tools
- Threat intelligence platforms
- Cloud security tools
- Log analysis tools
- Digital forensics tools
- Query and analytics platforms
A SIEM can provide centralized data, while EDR can provide detailed endpoint information.
For deeper investigations, analysts may also use computer forensics tools to examine digital evidence.
Threat Hunting and MITRE ATT&CK
MITRE ATT&CK is a knowledge base describing adversary tactics and techniques.
Security teams can use ATT&CK to:
- Develop hunting hypotheses
- Identify detection gaps
- Map observed behavior
- Improve security coverage
For example, a threat hunter can select an attacker technique and determine whether the organization’s available telemetry can reveal evidence of that behavior.
Threat Hunting Example
Imagine an organization notices unusual authentication activity.
A threat hunter creates the hypothesis that a compromised account may be accessing systems outside its normal pattern.
The analyst then:
- Reviews authentication logs.
- Identifies unusual login locations.
- Checks device information.
- Reviews account permissions.
- Examines related endpoint activity.
- Searches for additional suspicious access.
- Determines whether the activity is legitimate or malicious.
If compromise is confirmed, the organization can follow its incident response plan to contain and remediate the threat.
Common Threat Hunting Mistakes
Searching Without a Hypothesis
Unfocused searches can produce large amounts of irrelevant data.
Relying Only on IOCs
Attackers can change IP addresses, domains, and files.
Ignoring Normal Behavior
Analysts need a baseline to determine whether activity is genuinely unusual.
Using Poor-Quality Data
Incomplete logging can create major visibility gaps.
Treating Every Anomaly as Malicious
Unusual activity requires investigation. An anomaly is not automatically an attack.
Threat Hunting Best Practices
Organizations can improve threat hunting by:
- Create clear hunting hypotheses.
- Maintain useful security telemetry.
- Understand normal activity.
- Use threat intelligence.
- Hunt for attacker behaviors.
- Combine multiple data sources.
- Document findings.
- Turn discoveries into detection rules.
- Review hunting results regularly.
- Coordinate hunting with incident response.
Successful threat hunting is an ongoing process rather than a one-time security exercise.
Threat Hunting Checklist
Before starting a hunt, ask:
- What threat am I looking for?
- What is my hypothesis?
- Which systems could be affected?
- What data is available?
- What does normal activity look like?
- Which indicators or behaviors should I search for?
- How will suspicious findings be investigated?
- What happens if malicious activity is confirmed?
- Can the findings improve future detection?
Conclusion
Threat hunting techniques give security teams a proactive way to search for threats that automated security controls may not detect.
Hypothesis-driven, IOC-based, TTP-based, behavioral, anomaly-based, and threat intelligence-driven hunting can reveal suspicious activity across endpoints, networks, identities, and cloud environments.
Effective hunting depends on good telemetry, skilled analysis, useful threat intelligence, and a clear response process. The goal is not simply to find unusual activity. It is to determine whether that activity represents a genuine security threat and then improve defenses based on what was discovered.
When threat hunting identifies confirmed malicious activity, a well-tested incident response plan helps the organization contain and remediate the incident.
FAQs
What are threat hunting techniques?
Threat hunting techniques are proactive methods security professionals use to search for hidden cyber threats, suspicious behavior, and signs of compromise.
What is the most common threat hunting technique?
Hypothesis-driven hunting is a common approach. Analysts begin with a security question and search available data for evidence that supports or disproves the hypothesis.
What is IOC-based threat hunting?
IOC-based hunting searches for known indicators of compromise, such as suspicious IP addresses, domains, URLs, and file hashes.
What is TTP-based threat hunting?
TTP-based hunting focuses on attacker behaviors and techniques rather than relying only on specific indicators that attackers can easily change.
What tools do threat hunters use?
Threat hunters commonly use SIEM, EDR, XDR, network monitoring, threat intelligence, cloud security, log analysis, and digital forensics tools.
Is threat hunting the same as threat detection?
No. Threat detection often involves automated systems identifying suspicious activity. Threat hunting is more proactive and involves analysts actively searching for threats.
How often should organizations perform threat hunting?
There is no single schedule for every organization. Mature security teams may conduct regular hunts and launch additional investigations when new threat intelligence or suspicious activity emerges.
What skills are needed for threat hunting?
Threat hunters benefit from knowledge of networking, operating systems, identity security, cloud environments, logs, threat intelligence, attacker techniques, and analytical thinking.



Network Detection and Response: Complete Guide
Modern cyberattacks can move through networks quickly. Attackers may use stolen credentials,...
Zahra_Alialiali6 Mins read
Endpoint Detection and Response Tools: Complete Guide
Computers, laptops, servers, and other endpoints are common targets for cyberattacks. Attackers...
Zahra_Alialiali6 Mins read
Security Operations Center Tools: Complete Guide
A Security Operations Center, or SOC, monitors an organization's systems for suspicious...
Zahra_Alialiali6 Mins read
Incident Response Plan: Complete Cybersecurity Guide
A cyberattack can happen even when an organization has strong security controls....
Zahra_Alialiali6 Mins read



Leave a comment