

SOAR Security Explained: A Beginner’s Guide
 Zahra_AlialialiOctober 6, 20267 Mins read40
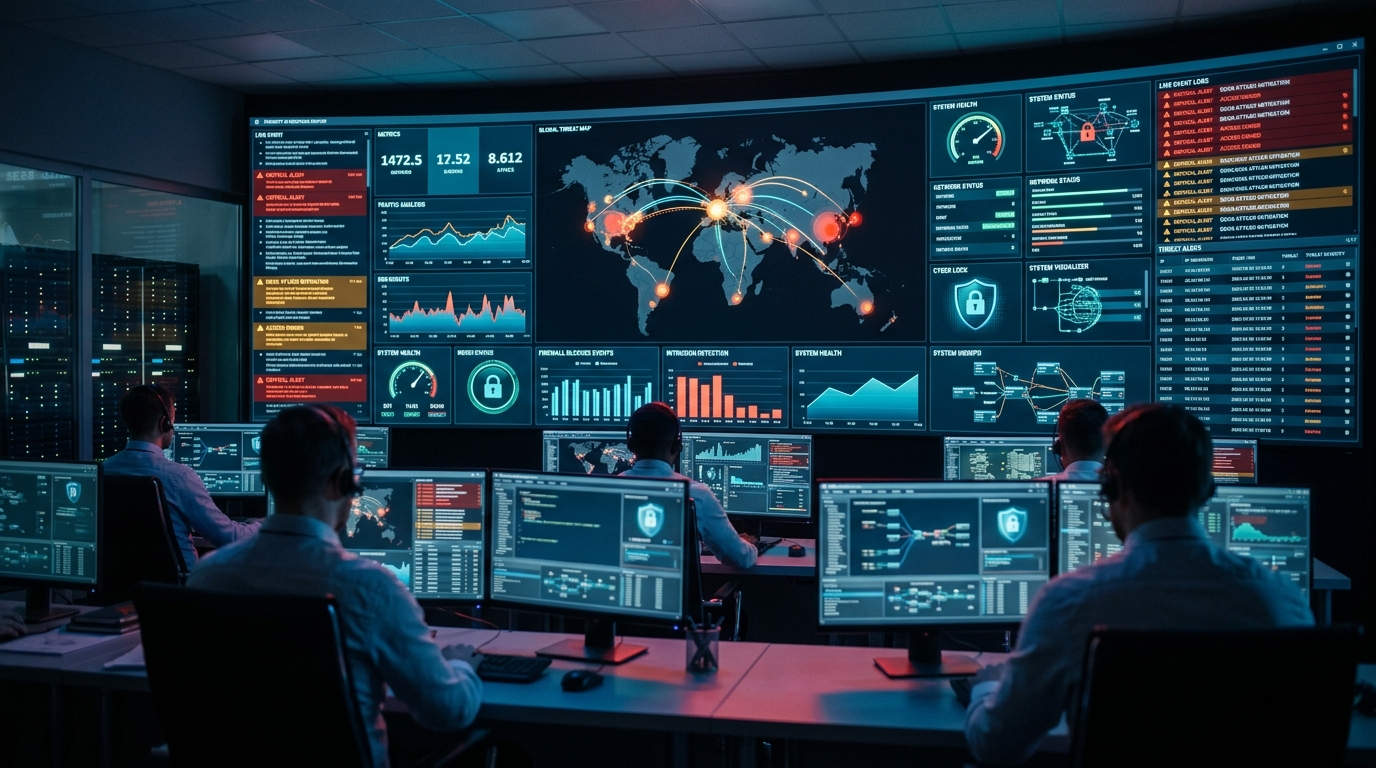
Security operations teams often manage many different tools at the same time. A SIEM collects security events, endpoint platforms monitor devices, firewalls protect networks, and threat intelligence platforms provide information about malicious activity.
Managing all these systems manually can take significant time. Analysts may spend hours investigating repetitive alerts, gathering information from different tools, and performing the same response steps repeatedly.
This is where SOAR security explained becomes useful.
SOAR stands for Security Orchestration, Automation and Response. It describes a security approach that connects different cybersecurity technologies, automates repeatable tasks, and helps security teams respond to incidents more efficiently.
SOAR does not replace security analysts. Instead, it gives them tools to automate predictable work while keeping people involved in important security decisions.
Organizations can also connect SOAR with threat intelligence platforms to automatically gather additional information about suspicious indicators.
This guide explains SOAR security in simple terms, how it works, common use cases, benefits, limitations, and how it fits into modern security operations.
What Is SOAR Security?
SOAR security refers to using Security Orchestration, Automation and Response technologies and processes to coordinate security operations.
SOAR helps security teams connect different tools and create automated workflows.
For example, imagine a security analyst receives an alert about a suspicious IP address.
Without automation, the analyst might need to:
- Copy the IP address.
- Search multiple threat intelligence sources.
- Check firewall logs.
- Search endpoint activity.
- Create a ticket.
- Contact another team.
- Decide whether to block the address.
A SOAR workflow can automate many of these repetitive steps.
The analyst can then spend more time reviewing the evidence and deciding what action makes sense.
What Does SOAR Stand For?
SOAR has three main components.
Security Orchestration
Orchestration connects different security technologies.
A SOAR platform can communicate with systems such as:
- SIEM
- EDR
- XDR
- Firewalls
- Email security
- Threat intelligence
- Identity platforms
- Cloud security tools
- Ticketing systems
Instead of operating as isolated systems, these technologies can exchange information through automated workflows.
Security Automation
Automation allows predefined tasks to happen without requiring an analyst to perform every step manually.
Examples include:
- Checking an IP address
- Looking up a file hash
- Gathering user information
- Creating an incident ticket
- Enriching an alert
- Sending notifications
Automation can reduce repetitive work and help analysts investigate incidents faster.
Security Response
Response involves taking action after identifying a security event.
Depending on the organization’s policies, automated or analyst-approved actions might include:
- Blocking a malicious domain
- Isolating an endpoint
- Disabling a compromised account
- Removing a phishing email
- Escalating an incident
Organizations should carefully control high-impact automated actions to prevent legitimate users or systems from being disrupted.
How Does SOAR Security Work?
A typical SOAR workflow can follow several stages.
1. An Alert Is Generated
A security product detects suspicious activity.
For example, an EDR platform may detect unusual behavior on a workstation.
2. SOAR Receives the Alert
The SOAR platform receives information about the event.
This may include:
- Username
- IP address
- Device
- File hash
- Alert type
- Timestamp
3. The Alert Is Enriched
The platform can automatically collect additional information.
It may query:
- Threat intelligence
- DNS services
- Endpoint systems
- Identity platforms
- Security databases
This gives analysts more context.
4. A Playbook Runs
A predefined workflow determines what steps should happen next.
Some steps may run automatically, while others may require analyst approval.
5. The Incident Is Investigated
The security team reviews the available information and determines whether the event represents a genuine threat.
6. Response Takes Place
The workflow may recommend or perform an appropriate response.
7. Everything Is Documented
The platform can record actions, findings, and decisions for future review.
What Are SOAR Playbooks?
A SOAR playbook is a predefined sequence of actions for handling a particular security event.
Playbooks create consistency.
For example, a phishing playbook could:
- Receive a phishing alert.
- Extract URLs and attachments.
- Check suspicious links against threat intelligence.
- Analyze attachments.
- Search for other users who received the message.
- Remove confirmed malicious messages.
- Create an incident ticket.
- Notify the security team.
Instead of every analyst following a different process, the organization can create a standardized workflow.
SOAR Security Use Cases
SOAR can support many types of security operations.
Phishing Investigation
Phishing generates a large number of security alerts.
A SOAR workflow can automatically:
- Extract URLs
- Analyze attachments
- Check domains
- Search threat intelligence
- Identify affected users
- Create tickets
Understanding phishing meaning can also help security teams combine automated controls with employee awareness.
Malware Investigation
When an endpoint security system detects potential malware, SOAR can collect additional information.
It may retrieve:
- File hashes
- Process information
- Endpoint details
- Network connections
- Threat intelligence
This reduces the amount of manual investigation required.
Account Compromise
SOAR can help investigate suspicious account activity.
A workflow might automatically check:
- Recent login activity
- Geographic locations
- Authentication failures
- Device information
- Unusual access patterns
Organizations can connect these workflows with identity threat detection and response capabilities.
Suspicious Network Activity
When security monitoring detects a suspicious connection, SOAR can investigate the associated IP address or domain.
It may check:
- Reputation
- Previous activity
- Related indicators
- Internal connections
The results can then be presented to an analyst.
SOAR and SIEM
SOAR and SIEM are different technologies, but they work well together.
A SIEM primarily focuses on collecting, correlating, and analyzing security events.
SOAR focuses on coordinating tools and automating investigation and response workflows.
A typical process could look like:
SIEM detects → SOAR investigates → SOAR enriches → Analyst reviews → Response occurs
This combination can reduce the amount of manual work required from security analysts.
Organizations can use SIEM tools alongside SOAR to create a more connected security operations environment.
SOAR and EDR/XDR
EDR and XDR technologies detect suspicious activity across endpoints and other security environments.
SOAR can receive alerts from these systems and trigger predefined workflows.
For example:
- EDR detects suspicious malware behavior.
- SOAR receives the alert.
- SOAR gathers threat intelligence.
- It checks whether similar activity appears elsewhere.
- An analyst reviews the findings.
- The endpoint is isolated if the organization confirms the threat.
This approach can shorten investigation and response times.
SOAR and Threat Intelligence
Threat intelligence tells security teams about potential threats, while SOAR can help operationalize that information.
For example, a threat intelligence source may identify a malicious domain.
A SOAR workflow can automatically:
- Search internal logs
- Check whether users accessed the domain
- Identify affected systems
- Alert analysts
- Update approved security controls
This turns intelligence into practical security action.
Benefits of SOAR Security
Faster Response
Automation can reduce the time between detection and investigation.
Less Repetitive Work
Analysts can spend less time performing routine tasks.
Consistent Incident Handling
Playbooks provide standardized processes for common incidents.
Better Tool Integration
SOAR connects technologies that might otherwise operate independently.
Improved Investigation
Automated enrichment gives analysts more information when reviewing alerts.
Better Documentation
SOAR platforms can record investigation steps and response actions.
Limitations and Challenges
SOAR is useful, but it does not solve every security problem.
Poorly Designed Automation
An incorrectly designed workflow can produce unnecessary actions or false results.
Excessive Automation
Not every security decision should happen automatically.
High-impact actions may require human approval.
Complex Integrations
Connecting many security products can require technical expertise and ongoing maintenance.
Data Quality Problems
Automation depends on reliable information. Incorrect threat intelligence can lead to incorrect decisions.
Maintenance
Playbooks need regular testing and updating as security tools and business processes change.
How to Implement SOAR Security
Organizations should avoid trying to automate everything immediately.
Start With Repetitive Tasks
Identify tasks analysts perform frequently.
Good starting points include:
- Indicator enrichment
- Ticket creation
- Phishing analysis
- Reputation checks
- Alert notifications
Begin With Low-Risk Automation
Start with actions that are unlikely to cause disruption.
For example, automatically collecting information is generally safer than automatically disabling a user account.
Create Clear Playbooks
Each playbook should have:
- A defined trigger
- Clear actions
- Decision points
- Escalation rules
- Expected outcomes
Keep Humans Involved
Analysts should approve high-impact actions when appropriate.
Measure Results
Organizations can track:
- Investigation time
- Response time
- Analyst workload
- False positives
- Number of automated tasks
- Successful response actions
SOAR Security Best Practices
Organizations can improve their SOAR implementation by:
- Starting with clearly defined use cases
- Automating repetitive tasks
- Testing playbooks regularly
- Limiting high-risk automation
- Keeping integrations updated
- Reviewing false positives
- Documenting workflows
- Measuring performance
- Updating playbooks as threats change
The objective should be meaningful automation rather than automation for its own sake.
SOAR vs SIEM
The simplest difference is their primary purpose.
| Technology | Main Purpose |
|---|---|
| SIEM | Collects and analyzes security events |
| SOAR | Orchestrates tools and automates response |
| EDR | Detects and investigates endpoint activity |
| Threat Intelligence Platform | Collects and analyzes threat information |
These technologies can work together as part of a security operations program.
Future of SOAR Security
Artificial intelligence is likely to change SOAR capabilities significantly.
AI can help with:
- Alert prioritization
- Investigation summaries
- Threat correlation
- Pattern recognition
- Playbook recommendations
- Security analysis
AI may allow security teams to automate more complex investigation tasks.
However, organizations should maintain appropriate human oversight, especially when automated decisions could affect critical systems, accounts, or business operations.
SOAR will also become more closely connected with cloud security, identity protection, XDR, threat intelligence, and vulnerability management.
Conclusion
SOAR security explained simply means using orchestration, automation, and response capabilities to connect security tools and make security operations more efficient.
SOAR can automate repetitive investigation tasks, enrich alerts with additional information, coordinate multiple security products, and help analysts respond to incidents faster.
However, effective SOAR implementation requires careful planning. Organizations should start with well-defined use cases, test playbooks, maintain human oversight, and regularly improve their workflows.
Combining SOAR with continuous threat exposure management can also help organizations connect automated response with broader efforts to identify and reduce security exposure.
Ultimately, SOAR is not about replacing cybersecurity professionals. It is about giving them better automation, better context, and more time to focus on complex security decisions.
FAQs
What does SOAR mean in cybersecurity?
SOAR stands for Security Orchestration, Automation and Response. It connects security tools and automates predefined workflows to support investigation and incident response.
What is SOAR security used for?
SOAR can be used for phishing investigations, malware analysis, account compromise, threat intelligence enrichment, alert management, and other repetitive security operations.
Is SOAR the same as SIEM?
No. SIEM primarily collects and analyzes security events, while SOAR focuses on coordinating tools and automating security workflows.
What are SOAR playbooks?
SOAR playbooks are predefined workflows that specify what actions should occur when a particular security alert or incident is detected.
Can SOAR automatically block threats?
Yes, SOAR can perform approved automated actions such as blocking an indicator or isolating an endpoint. Organizations should use appropriate safeguards for high-impact actions.
Does SOAR replace security analysts?
No. SOAR supports security analysts by reducing repetitive work. Human judgment remains important for complex investigations and important response decisions.
How does SOAR work with threat intelligence?
SOAR can automatically send suspicious indicators to threat intelligence sources, collect additional context, and use the results to support investigation and response.
Is SOAR useful for small businesses?
It can be useful when a business has repetitive security workflows and multiple security tools, but organizations should consider their budget, staffing, and security requirements before adopting a SOAR platform.


Cloud Security Architecture: Complete Guide
Cloud environments give organizations flexibility, scalability, and access to powerful computing resources....
Zahra_Alialiali6 Mins read
Cloud Access Security Broker: Complete Guide
Cloud applications have become essential for modern businesses. Employees use SaaS platforms...
Zahra_Alialiali8 Mins read

Cloud Workload Protection Platform: Complete Guide
Cloud computing has changed how organizations build, deploy, and manage applications. Businesses...
Zahra_Alialiali7 Mins read
Security Orchestration Automation and Response
Security teams often use dozens of cybersecurity tools to protect an organization....
Zahra_Alialiali7 Mins read



Leave a comment