

What Is Cyber Threat Intelligence? A Complete Beginner Guide
 Zahra_AlialialiOctober 1, 20267 Mins read47
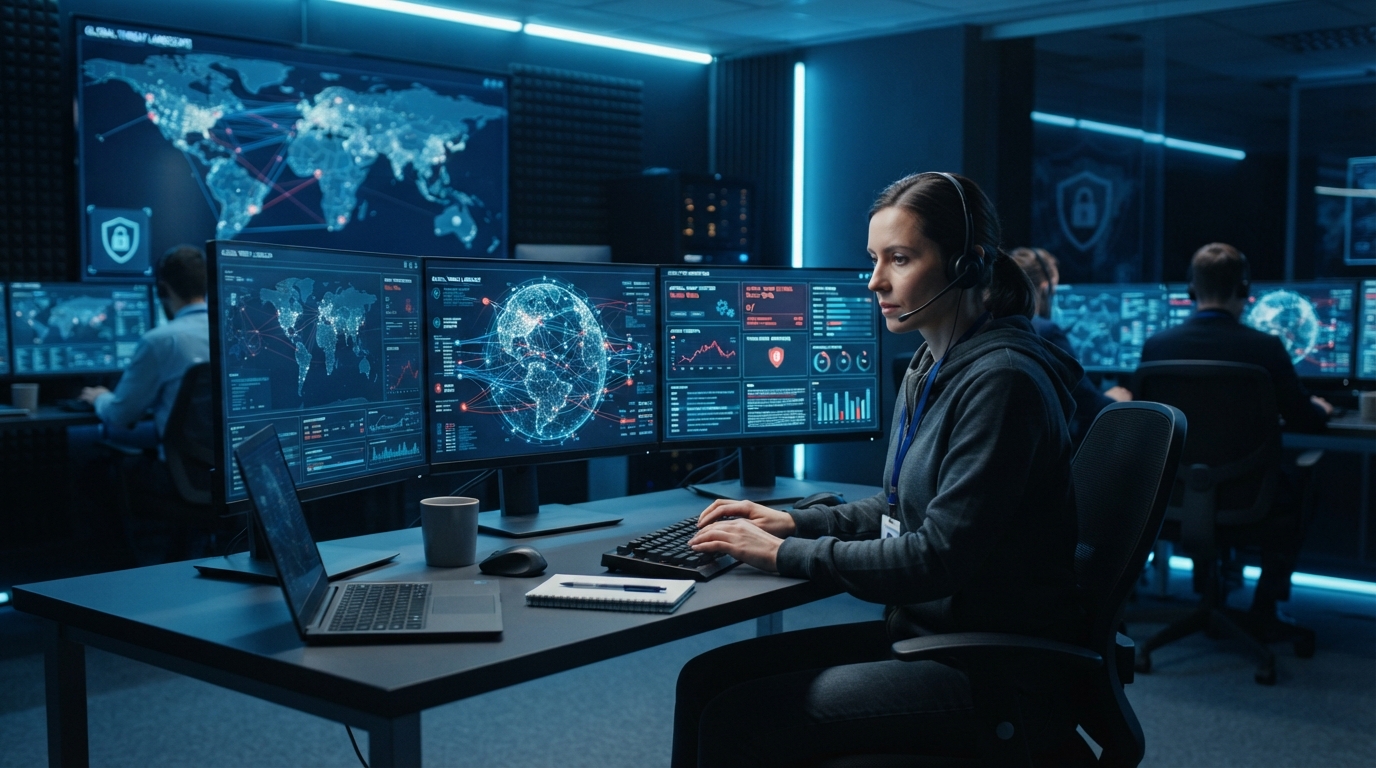
Cyber threats are becoming more advanced as attackers use new techniques to steal data, compromise accounts, exploit vulnerabilities, and disrupt businesses. Traditional security methods alone are often not enough because organizations need to understand not only what attacks are happening but also who is behind them, how they operate, and what steps can prevent future incidents.
This is where cyber threat intelligence becomes valuable.
So, what is cyber threat intelligence? It is the process of collecting, analyzing, and applying information about cyber threats to help organizations identify risks, improve defenses, and respond to attacks more effectively.
Threat intelligence helps security teams move from a reactive approach to a proactive security strategy. Instead of waiting for an attack to happen, organizations can use threat information to prepare defenses before attackers succeed.
Cyber threat intelligence works alongside technologies such as AI threat detection to identify suspicious activity, analyze patterns, and improve security decision-making.
This guide explains how cyber threat intelligence works, its different types, benefits, challenges, and how businesses use it to strengthen cybersecurity.
What Is Cyber Threat Intelligence?
Cyber threat intelligence is the practice of gathering and analyzing information about current and potential cyber threats.
The goal is to transform raw security information into useful knowledge that helps organizations make better security decisions.
Cyber threat intelligence can provide insights about:
- Cybercriminal groups
- Attack techniques
- Malware campaigns
- Vulnerabilities
- Malicious domains
- Suspicious IP addresses
- Data breaches
- Emerging threats
For example, if security researchers discover that attackers are actively exploiting a vulnerability in a popular application, organizations can use that information to prioritize patching and improve monitoring.
Threat intelligence helps security teams understand threats before they become major incidents.
Why Is Cyber Threat Intelligence Important?
Modern organizations face thousands of potential security risks.
Attackers constantly change their methods by using:
- Phishing campaigns
- Ransomware
- Credential theft
- Social engineering
- Cloud attacks
- Supply chain attacks
- Zero-day vulnerabilities
Without reliable intelligence, security teams may struggle to identify which risks require immediate attention.
Cyber threat intelligence helps organizations:
- Detect threats earlier
- Understand attacker behavior
- Improve incident response
- Prioritize vulnerabilities
- Strengthen security controls
- Reduce potential damage
For example, vulnerability scanners may identify hundreds of weaknesses, but threat intelligence can show which vulnerabilities attackers are actively targeting.
This allows security teams to focus resources where they matter most.
How Does Cyber Threat Intelligence Work?
Cyber threat intelligence follows a continuous process that helps organizations collect, analyze, and use threat information.
Threat Intelligence Lifecycle
Planning and Direction
The first step is understanding what information an organization needs.
Security teams may ask:
- Which threats target our industry?
- Which systems are most valuable?
- What attackers are targeting similar organizations?
- Which risks require immediate action?
Clear objectives help teams collect useful intelligence instead of gathering unnecessary information.
Data Collection
Security teams collect information from multiple sources.
Common sources include:
- Security researchers
- Threat intelligence providers
- Government reports
- Malware analysis
- Internal security logs
- Vulnerability databases
- Industry communities
Collected information may include:
- Malware samples
- Attack patterns
- Indicators of compromise
- Attacker infrastructure
- Vulnerability details
Data Analysis
Raw information is not automatically useful.
Security analysts evaluate data to determine:
- Is the threat legitimate?
- How serious is the risk?
- Who may be responsible?
- What systems are affected?
- What defensive actions are required?
Analysts combine multiple sources to create a clearer picture of potential threats.
Intelligence Sharing and Action
After analysis, useful intelligence is shared with relevant teams.
For example:
- Security analysts may receive technical indicators.
- Executives may receive risk summaries.
- IT teams may receive recommended security actions.
The goal is to turn intelligence into practical improvements.
Types of Cyber Threat Intelligence
Cyber threat intelligence is commonly divided into four main categories.
Strategic Threat Intelligence
Strategic intelligence focuses on high-level cybersecurity trends and risks.
It helps decision-makers understand:
- Long-term threat patterns
- Industry risks
- Cybercrime trends
- Business impact
Executives often use strategic intelligence when planning security investments.
Tactical Threat Intelligence
Tactical intelligence focuses on attacker methods and techniques.
It helps security teams understand:
- How attackers operate
- Which tactics they use
- What security controls can stop them
The MITRE ATT&CK framework is commonly used to map attacker techniques and behaviors.
Technical Threat Intelligence
Technical intelligence focuses on specific technical details.
Examples include:
- Malware hashes
- Malicious IP addresses
- Suspicious domains
- URLs
- File signatures
Security tools can use this information to detect and block known threats.
Operational Threat Intelligence
Operational intelligence focuses on active attacks and campaigns.
It may provide information about:
- Attack timing
- Target selection
- Campaign methods
- Attacker activity
This helps organizations prepare for specific threats.
Sources of Cyber Threat Intelligence
Organizations use different sources to collect threat information.
Open Source Intelligence (OSINT)
OSINT uses publicly available information.
Examples include:
- Security blogs
- Research reports
- Vulnerability databases
- Public threat reports
OSINT can provide valuable information when analysts verify the accuracy of findings.
Internal Security Data
Organizations can create intelligence from their own environment.
Examples include:
- Previous incidents
- Security alerts
- Network activity
- User behavior
- Malware investigations
Internal data helps companies understand their unique risks.
Threat Intelligence Platforms
Threat intelligence platforms help organizations collect, organize, and analyze security information.
They can integrate with:
- SIEM platforms
- EDR solutions
- Firewalls
- Security monitoring tools
These platforms help teams manage large amounts of threat data efficiently.
Cyber Threat Intelligence and Indicators of Compromise
Indicators of compromise (IOCs) are signs that may suggest malicious activity.
Common examples include:
- Suspicious IP addresses
- Malicious domains
- Malware file hashes
- Unusual network connections
- Known attack patterns
Security teams use IOCs to search for possible infections and block known threats.
However, attackers frequently change their infrastructure, so organizations should combine IOCs with behavioral analysis.
Cyber Threat Intelligence vs Threat Hunting
Although both activities focus on finding threats, they serve different purposes.
Cyber Threat Intelligence
Threat intelligence provides information about:
- Attackers
- Techniques
- Malware
- Emerging risks
It helps organizations understand what threats they should prepare for.
Threat Hunting
It involves actively searching an environment for hidden threats.
Threat hunters investigate:
- Suspicious activity
- Unusual behavior
- Possible compromises
Threat hunters often use cyber threat intelligence to guide their investigations.
Cyber Threat Intelligence and Security Tools
Threat intelligence becomes more powerful when combined with cybersecurity technologies.
Security teams often integrate intelligence with:
- SIEM platforms
- EDR and XDR solutions
- Firewalls
- Security monitoring systems
For example, threat intelligence can help security software recognize known malicious activity and improve detection accuracy.
Modern cybersecurity software often uses threat intelligence feeds to provide better protection against evolving attacks.
Benefits of Cyber Threat Intelligence
Organizations gain several advantages by using threat intelligence.
Faster Threat Detection
Threat intelligence helps teams recognize suspicious activity earlier.
Better Risk Prioritization
Organizations can focus on threats that create the greatest risk.
Improved Incident Response
Security teams can respond faster when they understand attacker methods.
Stronger Security Decisions
Threat intelligence provides evidence-based insights instead of relying on assumptions.
Reduced Attack Impact
Understanding threats helps organizations improve prevention and response strategies.
Challenges of Cyber Threat Intelligence
Although threat intelligence provides significant value, organizations face several challenges.
Too Much Information
Security teams may receive large amounts of threat data.
The challenge is identifying what information is useful.
False Intelligence
Not every security report is accurate.
Analysts must verify information before taking action.
Limited Resources
Small organizations may lack the staff needed to analyze intelligence effectively.
Constantly Changing Threats
Attackers continuously modify their techniques, requiring organizations to update their intelligence regularly.
Role of Artificial Intelligence in Cyber Threat Intelligence
Artificial intelligence is changing how organizations analyze threats.
AI can help with:
- Detecting patterns
- Analyzing large datasets
- Identifying suspicious behavior
- Prioritizing alerts
- Supporting malware analysis
AI allows security teams to process information faster.
However, human expertise remains important because security decisions require context and judgment.
How Businesses Can Implement Cyber Threat Intelligence
Organizations can start by following several steps.
Identify Security Goals
Determine what information is most valuable.
Select Reliable Sources
Use trusted intelligence providers and security research.
Integrate With Security Tools
Connect intelligence with:
- SIEM
- EDR
- Firewalls
- Monitoring platforms
Train Security Teams
Analysts need the skills to interpret and apply intelligence effectively.
Continuously Improve
Threat intelligence programs should evolve as threats change.
Common Cyber Threat Intelligence Mistakes
Collecting Data Without Action
Information has little value unless organizations use it to improve security.
Depending on One Source
Using multiple reliable sources creates better visibility.
Ignoring Internal Threat Data
Organizations should analyze their own security events as well.
Focusing Only on Malware
Threat intelligence should cover identities, vulnerabilities, infrastructure, and attacker behavior.
Cyber Threat Intelligence Checklist
Organizations should ask:
- Do we understand threats targeting our industry?
- Do we collect intelligence from reliable sources?
- Do we monitor indicators of compromise?
- Do we integrate intelligence with security tools?
- Do teams know how to use threat information?
- Do we update intelligence regularly?
- Do we use intelligence to improve defenses?
Future of Cyber Threat Intelligence
Cyber threats will continue evolving as organizations adopt:
- Cloud computing
- Artificial intelligence
- Automation
- IoT devices
- Digital platforms
Future threat intelligence programs will become more automated and predictive.
AI-powered systems may help analysts identify emerging threats faster and improve security operations.
However, successful threat intelligence will still depend on skilled professionals, reliable information, and effective security processes.
Conclusion
Understanding what is cyber threat intelligence helps organizations move from reactive cybersecurity toward proactive defense.
Threat intelligence allows security teams to understand attackers, identify risks, improve detection, and respond more effectively to cyber incidents.
By combining threat intelligence with security technologies and approaches such as continuous threat exposure management, organizations can discover weaknesses, prioritize risks, and strengthen their overall security posture.
Ultimately, cyber threat intelligence is not only about collecting information. It is about transforming data into actionable knowledge that helps organizations build stronger defenses against modern cyber threats.
FAQs
What is cyber threat intelligence?
Cyber threat intelligence is the process of collecting, analyzing, and using information about cyber threats to help organizations improve security decisions.
Why is cyber threat intelligence important?
It helps organizations detect threats earlier, understand attackers, prioritize risks, and improve incident response.
What are the four types of cyber threat intelligence?
The four main types are strategic, tactical, technical, and operational threat intelligence.
What are indicators of compromise?
Indicators of compromise are technical signs that may show a system has been affected by malicious activity.
What is the difference between threat intelligence and threat hunting?
Threat intelligence provides information about threats, while threat hunting actively searches systems for hidden attacks.
How does AI improve cyber threat intelligence?
AI helps analyze large amounts of security data, identify patterns, and support faster threat detection.
What tools use cyber threat intelligence?
SIEM platforms, EDR/XDR solutions, firewalls, and cybersecurity software often integrate threat intelligence.
How can businesses start using cyber threat intelligence?
Businesses can begin by identifying security goals, choosing reliable intelligence sources, integrating tools, and training security teams.




Cloud Access Security Broker: Complete Guide
Cloud applications have become essential for modern businesses. Employees use SaaS platforms...
Zahra_Alialiali8 Mins read
Cloud Workload Protection Platform: Complete Guide
Cloud computing has changed how organizations build, deploy, and manage applications. Businesses...
Zahra_Alialiali7 Mins read
SOAR Security Explained: A Beginner’s Guide
Security operations teams often manage many different tools at the same time....
Zahra_Alialiali7 Mins read
Security Orchestration Automation and Response
Security teams often use dozens of cybersecurity tools to protect an organization....
Zahra_Alialiali7 Mins read


Leave a comment