

Cybersecurity Risk Assessment: Complete Guide
 Zahra_AlialialiOctober 28, 20266 Mins read16
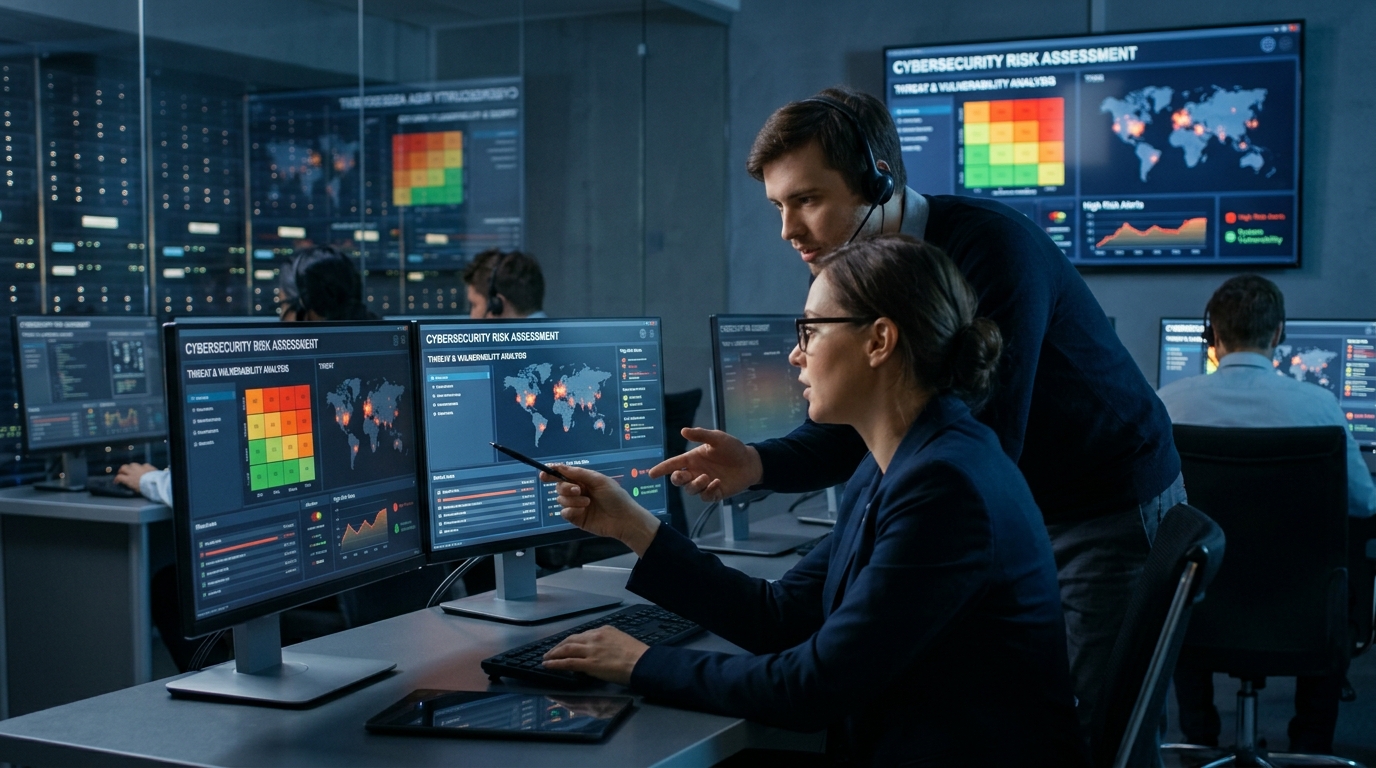
Every organization faces cybersecurity risks. These risks can come from malware, phishing, weak passwords, vulnerable software, insider threats, cloud misconfigurations, and third-party services.
However, not every risk has the same level of impact.
A small security issue on a test system may have little effect. A similar weakness on a critical production server could cause serious damage.
A cybersecurity risk assessment helps organizations understand these differences. It identifies important assets, evaluates potential threats, estimates their impact, and helps security teams decide which risks need attention first.
It also works alongside the vulnerability management lifecycle, which focuses more specifically on identifying and reducing technical vulnerabilities.
This guide explains how cybersecurity risk assessments work, the main steps involved, common frameworks, and best practices.
What Is a Cybersecurity Risk Assessment?
A cybersecurity risk assessment is a structured process used to identify, analyze, and prioritize risks that could affect an organization’s information systems and data.
The process usually considers three key questions:
- What could go wrong?
- How likely is it to happen?
- What would the impact be?
Security teams can then determine which risks require immediate action and which can be monitored or accepted.
The assessment should consider technology, people, processes, data, and third-party relationships.
Why Is a Cybersecurity Risk Assessment Important?
Organizations cannot protect every system in exactly the same way.
A risk assessment helps security teams focus their resources where they can make the biggest difference.
It can help organizations:
- Identify important security risks
- Protect critical assets
- Prioritize security investments
- Improve security controls
- Support compliance efforts
- Reduce potential business damage
- Prepare for cybersecurity incidents
Regular assessments can also reveal new risks as technology and business operations change.
Cybersecurity Risk Assessment vs Vulnerability Assessment
These terms are related but have different purposes.
A vulnerability assessment focuses mainly on identifying weaknesses in systems, applications, networks, and devices.
A cybersecurity risk assessment takes a broader view.
It considers:
- Assets
- Threats
- Vulnerabilities
- Likelihood
- Business impact
- Existing controls
- Third-party risks
For example, a vulnerability scanner might identify an outdated application.
A risk assessment goes further by asking how important that application is, whether it is exposed to attackers, and what could happen if the vulnerability were exploited.
Key Components of a Cybersecurity Risk Assessment
Asset Identification
The first step is understanding what needs protection.
Assets may include:
- Customer information
- Financial records
- Servers
- Applications
- Cloud resources
- Employee devices
- Intellectual property
- Business-critical systems
Organizations should identify which assets are most important to business operations.
Threat Identification
Next, security teams identify potential threats.
Examples include:
- Phishing
- Ransomware
- Malware
- Credential theft
- Insider threats
- Denial-of-service attacks
- Supply chain attacks
- Cloud account compromise
Threats can come from both external and internal sources.
Vulnerability Identification
Security teams then look for weaknesses that could be exploited.
These may include:
- Unpatched software
- Weak passwords
- Excessive permissions
- Misconfigured cloud resources
- Unsupported systems
- Poor security policies
Vulnerability management can provide valuable information during this stage.
Impact Assessment
The organization should determine what could happen if a threat succeeds.
Potential impacts include:
- Financial losses
- Data exposure
- Service disruption
- Legal consequences
- Regulatory penalties
- Reputation damage
Critical business systems usually require stronger protection because their failure could have a greater impact.
Likelihood Assessment
Security teams also estimate how likely a risk is to occur.
Factors may include:
- Exposure to the internet
- Attacker interest
- Existing security controls
- Exploit availability
- Historical incidents
- Employee behavior
A highly damaging risk that is also likely to occur should receive significant attention.
How to Perform a Cybersecurity Risk Assessment
1. Define the Scope
Decide which systems, departments, locations, applications, or business processes will be assessed.
A clear scope prevents important areas from being overlooked.
2. Identify Assets
Create an inventory of important hardware, software, data, accounts, and services.
Cloud environments should also be included.
3. Identify Threats
Consider which threats could affect each important asset.
The risks will vary depending on the organization’s industry and technology environment.
4. Identify Vulnerabilities
Review weaknesses that attackers could potentially exploit.
Security testing, vulnerability scanning, configuration reviews, and audits can help.
5. Evaluate Risk
Estimate the likelihood and potential impact of each risk.
A simple approach is to categorize risks as:
- Low
- Medium
- High
- Critical
More mature programs may use quantitative methods or detailed risk scoring.
6. Prioritize Risks
Address the risks that could cause the greatest damage first.
A risk involving a critical internet-facing system may deserve immediate action.
7. Select Security Controls
Choose appropriate controls to reduce the identified risks.
These may include:
- Multi-factor authentication
- Encryption
- Access controls
- Endpoint security
- Network monitoring
- Backups
- Security awareness training
Cloud environments may require additional controls. A strong cloud security architecture can help reduce risks across cloud workloads, identities, networks, and data.
8. Monitor and Review
Risk assessments should not be treated as one-time exercises.
New vulnerabilities, applications, threats, and business processes can change the risk level.
Organizations should therefore review their assessments regularly.
Cybersecurity Risk Assessment Frameworks
Several established frameworks can help organizations structure their assessments.
NIST Cybersecurity Framework
The NIST Cybersecurity Framework provides guidance for managing cybersecurity risk.
Organizations can use it to understand their current security posture, identify gaps, and establish improvement priorities.
ISO 27001 and ISO 27005
It provides requirements for an information security management system.
ISO 27005 provides guidance specifically related to information security risk management.
Organizations can use these standards to create structured and repeatable risk management processes.
Third-Party Cybersecurity Risk
An organization’s security does not depend only on its own systems.
Vendors, contractors, cloud providers, and other partners can introduce additional risks.
Third-party assessments may examine:
- Security controls
- Data handling
- Access permissions
- Incident response
- Compliance
- Business continuity
Organizations should understand which vendors have access to sensitive information or critical systems.
Cybersecurity Risk Assessment in Cloud Environments
Cloud adoption creates new risk considerations.
Organizations should assess:
- Cloud identities
- Access permissions
- Storage configuration
- APIs
- Network controls
- Workloads
- Logging
- Data protection
Cloud risks can change quickly because resources may be created, modified, or removed frequently.
Continuous monitoring is therefore important.
Common Cybersecurity Risk Assessment Mistakes
Ignoring Important Assets
An incomplete asset inventory can leave critical systems outside the assessment.
Treating Every Risk Equally
Not every vulnerability or threat requires the same response.
Focusing Only on Technology
People and processes can create major security risks too.
Using Outdated Information
Old assessments may not reflect current systems or threats.
Ignoring Third Parties
A vendor with access to sensitive data can create significant exposure.
Failing to Act on Findings
An assessment has little value if identified risks are never addressed.
Cybersecurity Risk Assessment Best Practices
Organizations can improve their risk assessments by:
- Maintain an accurate asset inventory.
- Identify critical business systems.
- Consider both internal and external threats.
- Include third-party risks.
- Use current threat intelligence.
- Prioritize risks by business impact.
- Document existing security controls.
- Assign risk owners.
- Set remediation deadlines.
- Review assessments regularly.
- Test important security controls.
A strong assessment should lead to practical security improvements.
Cybersecurity Risk Assessment Checklist
Use this checklist when reviewing your program:
- Have all important assets been identified?
- Are critical data and systems clearly defined?
- Have major threats been documented?
- Have vulnerabilities been evaluated?
- Has business impact been considered?
- Has likelihood been assessed?
- Are risks ranked by priority?
- Are risk owners assigned?
- Are appropriate controls in place?
- Are third-party risks included?
- Is the assessment updated regularly?
- Are high-priority risks being addressed?
How AI Can Support Cybersecurity Risk Assessment
Artificial intelligence can help security teams process large amounts of security information.
AI may assist with:
- Identifying unusual patterns
- Correlating security events
- Prioritizing risks
- Analyzing vulnerability data
- Summarizing security findings
However, AI should support rather than replace professional judgment.
Risk decisions can involve business, legal, financial, and operational factors that require human review.
Conclusion
A cybersecurity risk assessment helps organizations understand which threats and weaknesses could have the greatest impact on their systems, data, and business operations.
The process starts with identifying assets and threats. It then evaluates vulnerabilities, likelihood, and potential impact. Finally, organizations prioritize risks and select appropriate security controls.
Regular assessments are important because cybersecurity environments constantly change. New vulnerabilities, cloud services, vendors, and attack techniques can introduce new risks.
Organizations should also connect risk assessment findings with their incident response plan so that high-impact incidents can be handled quickly when they occur.
Ultimately, the goal is not to eliminate every possible risk. It is to understand risk clearly, prioritize it intelligently, and reduce the threats that matter most.
FAQs
What is a cybersecurity risk assessment?
A cybersecurity risk assessment is a structured process for identifying, analyzing, and prioritizing risks that could affect an organization’s systems, data, and operations.
Why is cybersecurity risk assessment important?
It helps organizations understand their most important security risks and decide where to focus security resources.
What are the main steps in a cybersecurity risk assessment?
The main steps include defining the scope, identifying assets, identifying threats and vulnerabilities, assessing likelihood and impact, prioritizing risks, selecting controls, and monitoring results.
What is the difference between risk assessment and vulnerability assessment?
Vulnerability assessment focuses mainly on technical weaknesses. Risk assessment considers the broader business risk created by threats, vulnerabilities, likelihood, impact, and existing controls.
How often should a cybersecurity risk assessment be performed?
The appropriate frequency depends on the organization. Assessments should be performed regularly and whenever major changes occur in systems, business operations, threats, or regulations.
What frameworks can be used for cybersecurity risk assessment?
Organizations can use frameworks and standards such as the NIST Cybersecurity Framework, ISO 27001, and ISO 27005 to structure cybersecurity risk management.
What is third-party cybersecurity risk?
Third-party cybersecurity risk is the risk introduced by vendors, contractors, cloud providers, and other external organizations that access systems, data, or services.
Can small businesses perform cybersecurity risk assessments?
Yes. Small businesses can perform simpler assessments by identifying their most important systems and data, reviewing major threats and vulnerabilities, and prioritizing the risks that could cause the greatest damage.




Vulnerability Management Lifecycle: Complete Guide
Every organization has security weaknesses. Some may come from outdated software, misconfigured...
Zahra_Alialiali5 Mins read
Network Detection and Response: Complete Guide
Modern cyberattacks can move through networks quickly. Attackers may use stolen credentials,...
Zahra_Alialiali6 Mins read
Endpoint Detection and Response Tools: Complete Guide
Computers, laptops, servers, and other endpoints are common targets for cyberattacks. Attackers...
Zahra_Alialiali6 Mins read

Threat Hunting Techniques: Complete Guide
Cybersecurity tools can detect many threats automatically, but they cannot always identify...
Zahra_Alialiali6 Mins read



Leave a comment