

Cloud Misconfiguration Examples: Complete Guide
 Zahra_AlialialiNovember 9, 20266 Mins read27
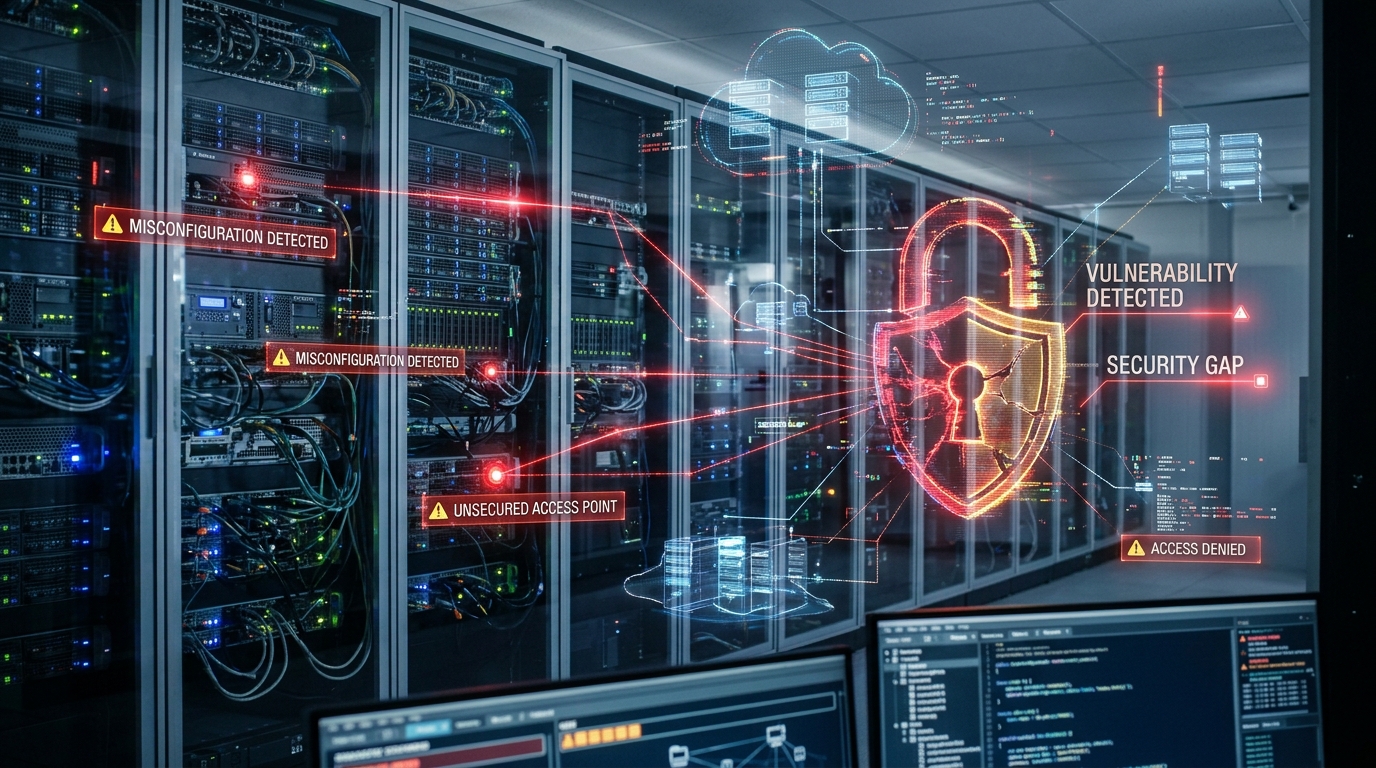
Cloud platforms make it easier for organizations to store data, run applications, and scale their infrastructure. However, a simple configuration mistake can create a serious security weakness.
Common cloud misconfiguration examples include publicly exposed storage, excessive permissions, open network ports, weak identity settings, and missing security controls.
These problems can expose sensitive information or give attackers unnecessary access to cloud resources. For this reason, organizations should include configuration security in their wider cloud security architecture strategy.
This guide explains common cloud misconfigurations, why they happen, how attackers can take advantage of them, and how organizations can prevent them.
What Is a Cloud Misconfiguration?
A cloud misconfiguration occurs when a cloud resource has an insecure or incorrect setting.
The problem may involve:
- Storage
- Identity and access
- Networks
- Databases
- APIs
- Containers
- Encryption
- Logging
- Security policies
Cloud platforms provide many security controls. However, the customer often needs to configure those controls correctly.
As a result, a secure cloud platform can still become vulnerable because of an incorrect setting.
Why Are Cloud Misconfigurations Dangerous?
Cloud environments can contain valuable information and critical applications.
A single configuration error could expose:
- Customer information
- Financial records
- Business documents
- Credentials
- Source code
- Application data
- Internal systems
Attackers constantly search for exposed cloud resources. Therefore, organizations should identify and correct configuration problems before attackers discover them.
Common Cloud Misconfiguration Examples
1. Publicly Accessible Cloud Storage
One of the most common examples involves cloud storage configured for public access.
A storage bucket may contain sensitive documents, backups, or application data. If its permissions allow anonymous access, anyone who discovers the resource may be able to view the information.
Organizations should regularly review storage permissions and ensure that public access remains disabled unless there is a legitimate business requirement.
2. Excessive IAM Permissions
Identity and Access Management (IAM) controls who can access cloud resources.
A common mistake is giving users, applications, or service accounts more permissions than they need.
For example, an application that only needs to read a database may receive permission to modify or delete data.
This increases the potential impact of a compromised account.
The principle of least privilege can significantly reduce this risk.
3. Open Network Ports
Cloud security groups and firewall rules control network access.
An administrator might accidentally expose a service to the public internet when it should only be available internally.
Open ports can increase an attacker’s ability to discover and target vulnerable services.
Security teams should review network rules regularly and restrict access to trusted sources whenever possible.
4. Exposed Cloud Databases
A database may become publicly accessible because of an incorrect network or access configuration.
If authentication controls are also weak, attackers could potentially access sensitive information.
Organizations should keep databases private whenever possible and restrict access through appropriate network controls.
5. Missing Encryption
Cloud platforms generally provide encryption capabilities, but organizations still need to configure and manage them appropriately.
Sensitive information may face greater exposure when encryption controls are missing or incorrectly configured.
Companies should identify which data requires encryption and ensure that encryption keys receive appropriate protection.
6. Weak IAM Authentication
Cloud accounts with weak authentication create another significant risk.
For example, an administrator account without multi-factor authentication could become a valuable target for attackers.
Organizations should enable MFA for privileged accounts and apply strong authentication policies across important cloud services.
7. Insecure APIs
Cloud applications often depend on APIs to communicate with other services.
An improperly secured API may expose sensitive information or allow unauthorized actions.
Common problems include weak authentication, excessive permissions, poor input validation, and unnecessary public exposure.
Developers should apply strong authentication and authorization controls to cloud APIs.
8. Poor Logging and Monitoring
A cloud environment can generate large amounts of security information.
If logging is disabled or poorly configured, security teams may struggle to detect suspicious activity.
Important events can include:
- Login attempts
- Permission changes
- API calls
- Data access
- Configuration changes
- Network activity
Organizations should enable appropriate logging and review important security events.
9. Misconfigured Backups
Cloud backups can contain large amounts of sensitive information.
If backup storage has weak permissions, attackers may target it to obtain copies of important data.
Backup systems should use appropriate access controls, encryption, monitoring, and retention policies.
10. Public Container Images
Container images may accidentally become publicly accessible.
A container image can also contain secrets, credentials, outdated software, or unnecessary components.
Organizations should scan container images before deployment and restrict access to private repositories.
11. Exposed Secrets
Developers sometimes store passwords, API keys, or access tokens in source code, configuration files, or cloud storage.
If attackers discover these secrets, they may gain access to cloud resources.
Organizations should use secure secrets management solutions and rotate credentials when exposure occurs.
12. Unnecessary Cloud Resources
Unused cloud resources can create hidden security risks.
For example, an old virtual machine or forgotten storage bucket may remain online after a project ends.
Attackers can target these forgotten assets because security teams may no longer monitor them closely.
Regular asset discovery helps organizations identify and remove unnecessary resources.
How Do Cloud Misconfigurations Happen?
Cloud misconfigurations can happen for several reasons.
Common causes include:
- Human error
- Poor documentation
- Rapid deployments
- Complex environments
- Incorrect permissions
- Lack of security testing
- Inconsistent policies
- Unused resources
- Misunderstood cloud settings
Automation can reduce some errors, but automated deployments also need security checks.
How to Find Cloud Misconfigurations
Security teams can use several methods to identify configuration problems.
Configuration Scanning
Cloud security tools can compare resources against security policies and known best practices.
Manual Reviews
Security teams can periodically review important permissions, network rules, storage settings, and other configurations.
Continuous Monitoring
Continuous monitoring can identify configuration changes soon after they occur.
Infrastructure as Code Scanning
Organizations using Infrastructure as Code can scan templates before deployment.
This approach can identify insecure settings before they reach production.
A cloud workload protection platform can also provide additional visibility into cloud workloads and security risks.
How to Prevent Cloud Misconfigurations
Apply Least Privilege
Give users and applications only the permissions they require.
Use MFA
Protect administrator and other sensitive accounts with multi-factor authentication.
Disable Unnecessary Public Access
Keep sensitive resources private unless public access serves a legitimate purpose.
Monitor Configuration Changes
Alert security teams when important settings change.
Automate Security Checks
Automated configuration checks can identify problems faster and reduce manual errors.
Review Cloud Resources Regularly
Remove unused accounts, services, storage, and other resources.
Protect Secrets
Store credentials and API keys in appropriate secrets management systems.
Use Security Policies
Create consistent configuration standards for cloud resources.
The Role of Cloud Security Tools
Organizations can use different security technologies to improve cloud visibility.
A cloud access security broker can help organizations apply security controls and gain visibility across supported cloud services.
Other tools can focus on workload security, identity, configuration management, data protection, and threat detection.
The best approach depends on the organization’s cloud environment and risk profile.
Cloud Misconfiguration Checklist
Use this checklist when reviewing a cloud environment:
- Is public access disabled for sensitive resources?
- Are IAM permissions limited?
- Is MFA enabled for privileged accounts?
- Are unnecessary ports closed?
- Are databases protected from public access?
- Is sensitive data encrypted?
- Are APIs properly secured?
- Is cloud activity logged?
- Are backups protected?
- Are secrets stored securely?
- Are unused resources removed?
- Are configuration changes monitored?
Common Cloud Security Mistakes
Organizations often focus on advanced threats while overlooking basic configuration problems.
For example, a company may invest in sophisticated security tools while leaving an unnecessary storage resource publicly accessible.
Similarly, excessive permissions can remain unnoticed for months.
Regular configuration reviews help prevent these simple weaknesses from becoming major security incidents.
Conclusion
The most important cloud misconfiguration examples include public storage, excessive IAM permissions, open network ports, exposed databases, weak authentication, insecure APIs, missing encryption, and poor monitoring.
These problems can expose sensitive information or provide attackers with unnecessary access to cloud resources.
Organizations can reduce the risk by applying least privilege, enabling MFA, restricting public access, protecting secrets, monitoring configuration changes, and regularly reviewing cloud resources.
Cloud security should also include a clear response process. If a configuration error leads to unauthorized access or data exposure, a documented cloud incident response process can help security teams investigate and contain the problem quickly.
Ultimately, cloud security depends not only on the provider’s technology but also on how carefully organizations configure and manage their own cloud environments.
FAQs
What is a cloud misconfiguration?
A cloud misconfiguration is an insecure or incorrect setting that can expose cloud resources, data, applications, or systems to unnecessary risk.
What is the most common cloud misconfiguration?
Publicly accessible storage is one common example. Excessive permissions and incorrectly configured network access are also frequent problems.
Can cloud misconfigurations cause data breaches?
Yes. An exposed storage resource, database, or poorly secured application can allow unauthorized people to access sensitive information.
How can companies detect cloud misconfigurations?
Organizations can use configuration scanners, cloud security tools, manual reviews, continuous monitoring, and Infrastructure as Code security checks.
What is the role of IAM in cloud security?
IAM controls who can access cloud resources and what actions they can perform. Proper IAM configuration helps prevent unauthorized access and excessive privileges.
How can organizations prevent cloud misconfiguration?
Organizations can use least privilege, MFA, configuration monitoring, automated security checks, regular reviews, and strong cloud security policies.
Are cloud misconfigurations only caused by employees?
No. Human error is common, but complex infrastructure, poor processes, automation errors, unclear policies, and rapidly changing environments can also contribute.
Why is continuous cloud monitoring important?
Cloud environments change frequently. Continuous monitoring helps organizations identify new configuration problems and suspicious changes before they create serious security exposure.

Ransomware Recovery Plan: Complete Guide
Ransomware can disrupt business operations, encrypt important files, and prevent employees from...
Zahra_Alialiali6 Mins read
Cryptocurrency: How Safe Is This Technology?
Cryptocurrency has changed how people send, receive, and invest money. It allows...
 Beatriz3 Mins read
Third-Party Risk Management in Cybersecurity: Complete Guide
Modern businesses depend on external vendors for cloud services, software, payment processing,...
Zahra_Alialiali6 Mins read

Insider Threat Detection: Complete Security Guide
Organizations invest heavily in protecting their networks from external attackers. However, security...
Zahra_Alialiali6 Mins read


Leave a comment