

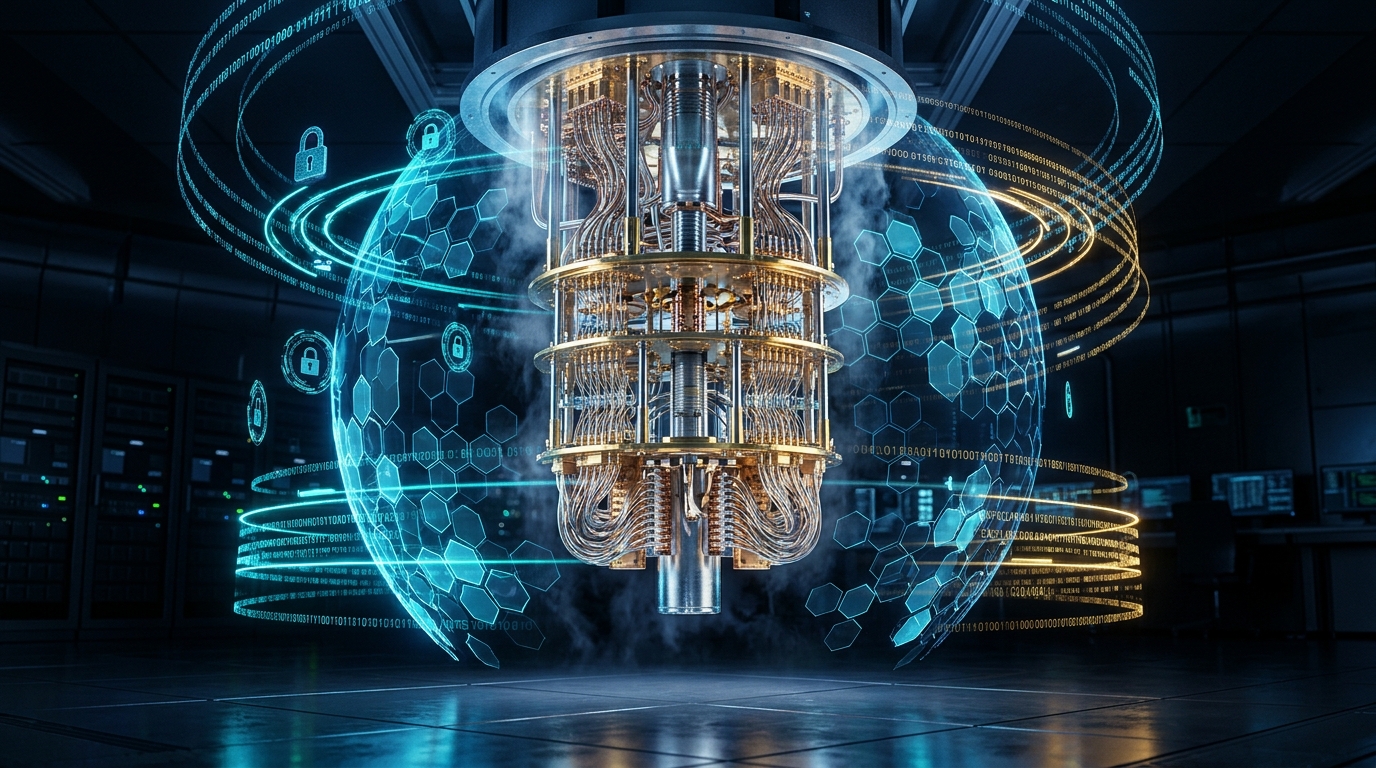
Modern businesses rely on encryption to protect financial information, passwords, communications, customer data, and other sensitive information. However, advances in quantum computing could eventually challenge some of today’s widely used cryptographic systems.
This is where post-quantum cryptography becomes important.
Post-quantum cryptography, often called PQC, focuses on developing cryptographic algorithms that can remain secure against attacks from both traditional and future quantum computers.
Organizations should consider this transition as part of long-term security planning. A broader cybersecurity risk assessment can help identify systems that depend on cryptography and determine where migration may be necessary.
What Is Post-Quantum Cryptography?
Post-quantum cryptography refers to cryptographic methods designed to resist attacks from sufficiently powerful quantum computers.
Traditional computers and quantum computers process information differently. Quantum computers could eventually solve certain mathematical problems much faster than conventional machines.
That creates a concern for cryptographic systems that rely on problems such as integer factorization and discrete logarithms.
PQC aims to provide security without requiring organizations to replace traditional computers with quantum devices.
Why Do Quantum Computers Threaten Encryption?
Many widely used public-key cryptographic systems rely on mathematical problems that are difficult for conventional computers to solve.
RSA and elliptic curve cryptography (ECC) are important examples.
A sufficiently capable quantum computer could use Shor’s algorithm to solve certain mathematical problems efficiently. This could undermine the security of RSA and ECC.
Symmetric encryption faces a different situation. Grover’s algorithm can theoretically reduce the security margin of certain symmetric cryptographic algorithms.
Therefore, quantum computing creates different challenges for different types of cryptography.
What Is Shor’s Algorithm?
Shor’s algorithm is a quantum algorithm that can efficiently solve integer factorization and discrete logarithm problems.
Those problems form the mathematical foundation of several widely used public-key cryptographic systems.
A sufficiently powerful quantum computer running Shor’s algorithm could therefore threaten systems such as RSA and ECC.
However, large-scale quantum computers capable of breaking current cryptography do not yet exist.
The concern comes from preparing for that possibility before it becomes a practical threat.
What Is Grover’s Algorithm?
Grover’s algorithm can speed up certain search problems on a quantum computer.
For cryptography, it can reduce the effective security of some symmetric encryption and hash-based systems.
The impact differs from Shor’s algorithm.
Organizations can often address this concern by using sufficiently large key sizes and appropriate cryptographic configurations.
What Cryptographic Systems Does PQC Replace?
Post-quantum cryptography primarily focuses on replacing or supplementing public-key systems that quantum computers could threaten.
These include cryptographic mechanisms used for:
- Key establishment
- Digital signatures
- Authentication
- Secure communications
The transition does not necessarily mean replacing every existing cryptographic algorithm immediately.
Instead, organizations need to identify vulnerable cryptographic dependencies and develop a migration strategy.
Post-Quantum Cryptography Algorithms
Modern PQC research has produced several promising approaches.
Lattice-Based Cryptography
Lattice-based techniques rely on mathematical problems involving lattices.
They have become an important foundation for several standardized post-quantum algorithms.
ML-KEM
ML-KEM is a standardized key-encapsulation mechanism designed to provide secure key establishment in a post-quantum environment.
Organizations can use such mechanisms to establish shared secrets between communicating parties.
ML-DSA
ML-DSA is a standardized digital signature algorithm designed to provide protection against quantum-capable attackers.
Digital signatures help verify authenticity and integrity.
Hash-Based Cryptography
Hash-based signatures rely on cryptographic hash functions rather than the mathematical problems used by RSA or ECC.
They represent another approach to post-quantum digital signatures.
Post-Quantum Cryptography vs Quantum Cryptography
These terms sound similar, but they describe different ideas.
Post-quantum cryptography uses mathematical algorithms that can run on conventional computers while aiming to resist quantum attacks.
Quantum cryptography uses principles of quantum physics to provide cryptographic capabilities.
One well-known example is quantum key distribution (QKD).
PQC is generally more practical for widespread software and infrastructure migration because organizations can deploy the algorithms on existing computing systems.
Harvest Now, Decrypt Later
One reason organizations should prepare early is the harvest now, decrypt later threat.
An attacker could collect encrypted information today and store it for future decryption.
If a sufficiently powerful quantum computer becomes available later, the attacker could potentially attempt to decrypt historical information that remains valuable.
This creates particular concerns for data that needs long-term confidentiality.
Examples include:
- Government information
- Intellectual property
- Financial records
- Sensitive business communications
- Long-term personal information
Organizations should therefore consider the required confidentiality period when assessing quantum risk.
How Organizations Can Prepare
Create a Cryptographic Inventory
Organizations should identify where cryptography is used.
This can include:
- Applications
- Websites
- VPNs
- Cloud services
- Databases
- Digital certificates
- APIs
- Devices
Without an inventory, organizations may struggle to identify vulnerable systems.
Identify High-Risk Data
Not every piece of encrypted information has the same long-term value.
Organizations should identify data that needs protection for many years.
Build Crypto-Agility
Crypto-agility means designing systems so cryptographic algorithms can be replaced without completely rebuilding the application.
This flexibility can make future migration much easier.
Work With Vendors
Third-party software and cloud providers may control important cryptographic components.
Organizations should ask vendors about their post-quantum migration plans and support for emerging standards.
Test New Algorithms
Organizations should evaluate post-quantum algorithms in controlled environments before deploying them broadly.
Performance, compatibility, key sizes, certificates, and infrastructure requirements all need consideration.
Post-Quantum Cryptography and Cloud Security
Cloud environments can contain many cryptographic dependencies.
Applications may rely on cloud services for:
- Encryption
- Key management
- Certificates
- Identity
- Secure communication
- Data storage
Organizations should understand which cryptographic technologies their cloud providers use and how those services will support post-quantum migration.
A strong cloud security architecture should therefore consider cryptographic agility and long-term data protection.
Challenges of Post-Quantum Migration
PQC migration will not happen instantly.
Organizations may face challenges such as:
- Legacy systems
- Incompatible software
- Large cryptographic inventories
- Vendor dependencies
- Performance changes
- Certificate management
- Staff knowledge gaps
Some systems may also be difficult to upgrade because they have long operational lifetimes.
Consequently, organizations should begin planning before quantum-resistant technology becomes an urgent requirement.
Post-Quantum Cryptography Best Practices
Organizations can prepare by:
- Inventorying cryptographic systems.
- Identifying quantum-vulnerable algorithms.
- Classifying long-term sensitive data.
- Developing a migration roadmap.
- Choosing crypto-agile technologies.
- Monitoring standards development.
- Working with technology vendors.
- Testing PQC algorithms.
- Training security and development teams.
- Reviewing legacy systems regularly.
A secure by design cybersecurity approach can also help organizations build cryptographic flexibility into new systems.
Post-Quantum Security Checklist
Ask these questions when preparing for the quantum era:
- Do we know where cryptography is used?
- Which systems depend on RSA or ECC?
- Which data requires long-term confidentiality?
- Do vendors have PQC migration plans?
- Can our applications replace cryptographic algorithms easily?
- Are legacy systems documented?
- Have we tested post-quantum algorithms?
- Do our cloud providers support migration planning?
- Have security teams received PQC training?
- Do we have a long-term migration roadmap?
Conclusion
Post-quantum cryptography is becoming an important part of long-term cybersecurity planning because sufficiently powerful quantum computers could threaten some widely used cryptographic systems.
RSA and ECC face significant theoretical risks from Shor’s algorithm, while symmetric cryptography faces different considerations related to Grover’s algorithm.
Organizations do not need to wait for a large-scale quantum computer before preparing. They can start by creating a cryptographic inventory, identifying long-term sensitive data, reviewing vendor dependencies, and improving crypto-agility.
The transition will take time, especially for organizations with complex infrastructure and legacy systems.
For that reason, quantum readiness should become part of broader security planning. Organizations should also monitor their LLM security risks as AI and quantum technologies continue to reshape the cybersecurity landscape.
Preparing early can make the eventual transition to quantum-resistant cryptography more manageable and reduce the risk of losing access to sensitive information when the threat landscape changes.
FAQs
What is post-quantum cryptography?
Post-quantum cryptography uses cryptographic algorithms designed to remain secure against attacks from sufficiently powerful quantum computers while running on conventional computing systems.
Why is post-quantum cryptography important?
Quantum computers could eventually threaten some widely used public-key cryptographic systems. PQC aims to provide alternatives that resist those attacks.
Does quantum computing break all encryption?
No. Quantum computers affect different cryptographic systems in different ways. Public-key algorithms such as RSA and ECC face significant theoretical risks, while symmetric encryption can generally address quantum risks through appropriate security margins.
What is Shor’s algorithm?
Shor’s algorithm is a quantum algorithm that can efficiently solve certain mathematical problems underlying cryptographic systems such as RSA and ECC.
What is Grover’s algorithm?
Grover’s algorithm provides a quantum speedup for certain search problems. It can reduce the effective security margin of some symmetric cryptographic systems.
What is ML-KEM?
ML-KEM is a standardized post-quantum key-encapsulation mechanism designed to support secure key establishment against quantum-capable attackers.
What does “harvest now, decrypt later” mean?
It describes an attack strategy in which adversaries collect encrypted information today and attempt to decrypt it in the future when sufficiently powerful technology becomes available.
How can businesses prepare for post-quantum cryptography?
Businesses can inventory their cryptographic systems, identify long-term sensitive data, review vendor plans, improve crypto-agility, test post-quantum algorithms, and develop a phased migration strategy.

Cryptographic Agility: Complete Cybersecurity Guide
Modern organizations rely on cryptography to protect data, applications, communications, and digital...
 Zahra_Alialiali6 Mins read
The Era of Home Drone Surveillance: What This Means for Your Home Security
The Era of Home Drone Surveillance: What This Means for Your Home...
 Beatriz4 Mins read
Neural Networks: How They Quietly Run Your Daily Life
The Code That Reads Your Mind: How Neural Networks Quietly Run Your...
Beatriz4 Mins read

Vibe Coding: What Is It and Why Do Developers Love It?
Imagine building a website by describing what you want instead of writing...
Beatriz4 Mins read


Leave a comment